Как удалить noscript из firefox
В мире Mozilla происходит много интересных событий. Но вам не нужно постоянно посещать новостные сайты, чтобы быть в курсе всех изменений. Зайдите на ленту новостей Mozilla Россия.
Страницы: 1
- Форумы
- » Поддержка пользователей
- » Как удалить установленный плагин NoScript ?
№1 20-11-2008 01:14:08

Kadet96 Группа: Guest UA: 2.0
Как удалить установленный плагин NoScript ?
Подскажите, как можно удалить установленный плагин NoScript ? В папке searchplugins его нет, и не могу найти его ни в одной папке Mozilla Firefox. Этот плагин мне мешает, не могу играть ни в одну браузерную игру. Пожалуйста помогите.
И еще вопрос, можно ли удалить браузерную или поисковую строку (не знаю как правильно) ICQ, которая всегда присутствует на странице?
№2 20-11-2008 04:46:00

Z&N Участник Группа: Members Зарегистрирован: 01-04-2008 Сообщений: 2401 UA: 3.1
Re: Как удалить установленный плагин NoScript ?

Kadet96 Панель Меню> Инструменты> Дополнения> NoScript
вообщето его можно просто отключить не удаляя и даже не совсем а только для сайта на котором он вам мешает-кликаете по иконке NoScript в статусбаре и выбитаете из контекстного меню Allow
Добавлено 20-11-2008 04:47:30
можно ли удалить браузерную или поисковую строку (не знаю как правильно) ICQ, которая всегда присутствует на странице?

что за строка ICQ и на какой странице ?
№3 20-11-2008 11:19:43
Kadet96 Группа: Guest UA: 2.0
Re: Как удалить установленный плагин NoScript ?
Спасибо огромное. Оказалось так просто. За одно и отключил эту строку ICQ, нашел в панели инструментов, просто снял галку и она исчезла. Еще раз спасибо.

А с этим плагином я вообще не понял для чего он Он вылезает на каждой странице и чего то блокирует, а в игру вообще не пускает. Прошу прощения за
№4 20-11-2008 11:23:48
Z&N Участник Группа: Members Зарегистрирован: 01-04-2008 Сообщений: 2401 UA: 3.1
Re: Как удалить установленный плагин NoScript ?
вообще не понял для чего он
Kadet96
для чего NoScript
Отредактировано Z&N (20-11-2008 11:24:11)
Аддон NoScript для Firefox

В Mozilla Firefox есть свои инструменты для защиты ПК. Теоретически они должны давать гарантию безопасности во время серфинга в интернете. На практике этих средств бывает не хватает, поэтому приходится искать дополнительные средства, в частности, устанавливать специальные дополнения. Одно из таких дополнений – NoScript для Firefox.
Немного о расширении
На чем основывается работа приложения? Принцип лежит в названии. Расширение блокирует скрипты: плагин JavaScript, а также Flash и Java.
Эти три модуля достаточно уязвимы. Их недостатками пользуются при создании различного рода вирусов. NoScript запрещает работу этих плагинов на всех ресурсах. Что делать, если у ресурса хорошая репутация и вы хотите посмотреть видео на нем, например? Ответ прост – добавлять его в список исключений.
Расширение также защищает от атак XSS, CSRF атак и ClickJacking. Это происходит за счет использования технологии ClearClick. NoScript еще умеет скрывать IP адрес.
Кстати, NoScript победил в 2006 PC World World Class Award. Инструмент защищает, более того, от рекламы – на сайтах перестают появляться раздражающие баннеры, которые зачастую мешают комфортной работе во всех обозревателях.
Скачиваем и устанавливаем
Дополнение загружается прямо в настройках обозревателя Firefox. Следуем инструкции.
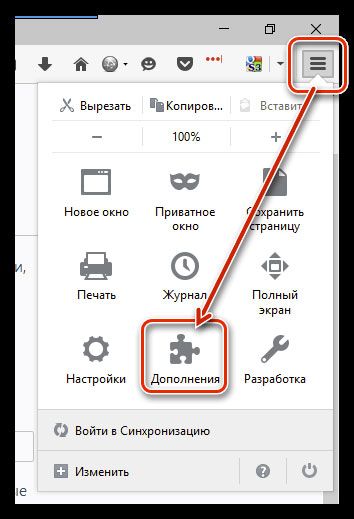
1.Находим иконку с тремя горизонтальными линиями, щелкаем по ней. В меню выбираем раздел «Дополнения» с иконкой пазла.
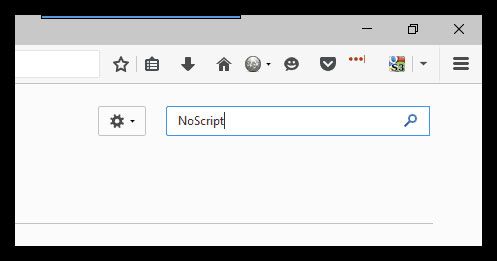
2.Перейдите на вкладку «Плагины» или «Расширения». В поисковую строку вводим название дополнения – NoScript.
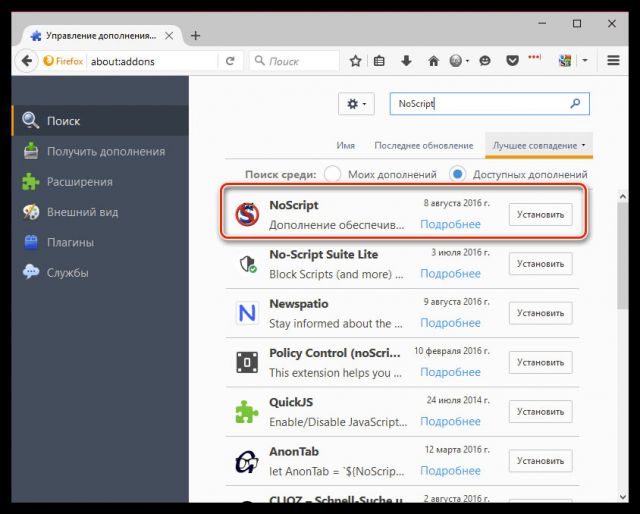
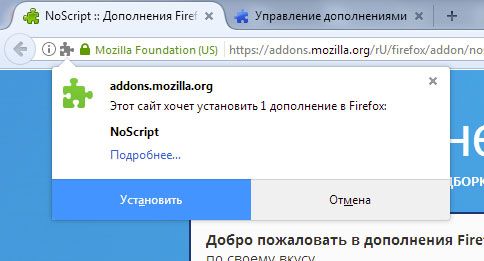
3.Выбираем первый пункт в результатах поиска. Для этого нажимаем на кнопку «Установить».
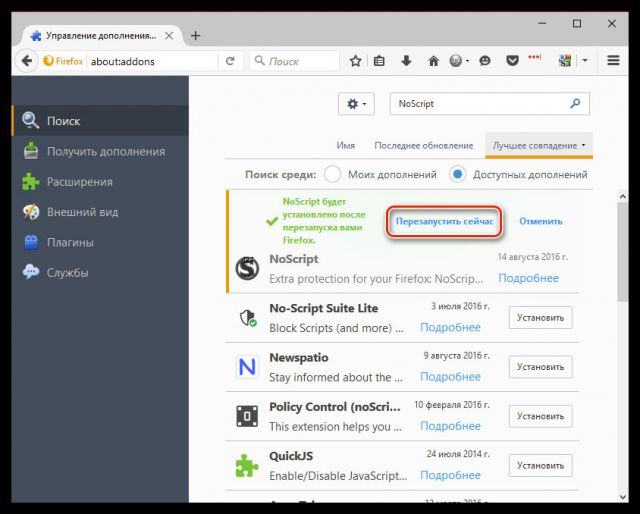
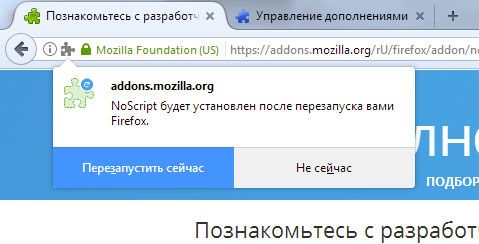
4.Чтобы расширение было добавлено в список активных, кликаем по кнопке «Перезапустить сейчас». Браузер закроется и откроется снова, но уже с установленным дополнением.
Установка через магазин
Альтернативный метод загрузки. Такой же легкий, как и предыдущий.
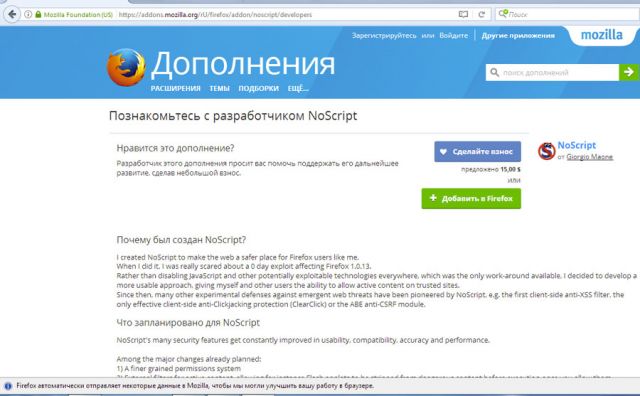
1.Перейдите по ссылке: https://addons.mozilla.org/rU/firefox/addon/noscript/.
2.Нажмите на «Добавить в Firefox». Подтвердите установку.
4.Перед этим можете также познакомиться ближе с расширением.
Как пользоваться NoScript?
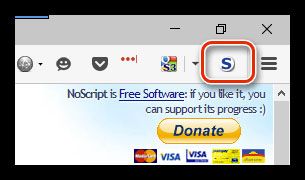
После повторного запуска обозревателя на верхней панели справа появится иконка NoScript Firefox. Она будет в виде круга с буквой S внутри.
Расширение уже активно выполняет свои функции по умолчанию, поэтому вы уже можете заметить, что некоторые элементы сайтов не открываются.
Настраиваем белый список
Плагины перестают функционировать автоматически на всех сайтах, что не совсем устраивает многих пользователей. Если вам нужны плагины на определенных сайтах, создайте свой список исключений и на этих ресурсах модули заработают. Как же настроить список?
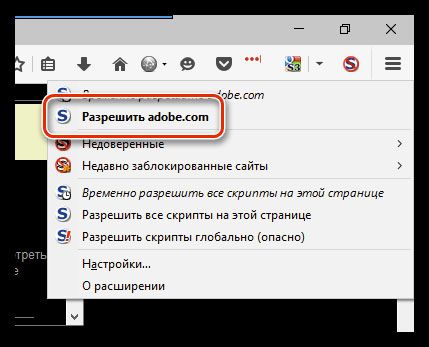
Вы посетили сайт, на котором необходима работа JavaScript. Кликните по иконке расширения – появится меню. Нажмите на строку «Разрешить…» и на сайте дополнение перестанет блокировать плагины. Вы также можете временно разрешить запускать модули. Для этого кликните по первой кнопке.
Если у вас на примете много надежных сайтов, для которых требуется работа плагинов, включите их в белый список.
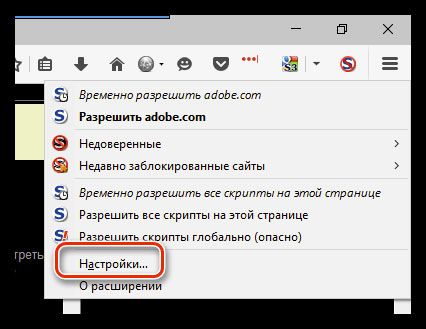
1.Кликните по иконке и выберите строку «Настройки».
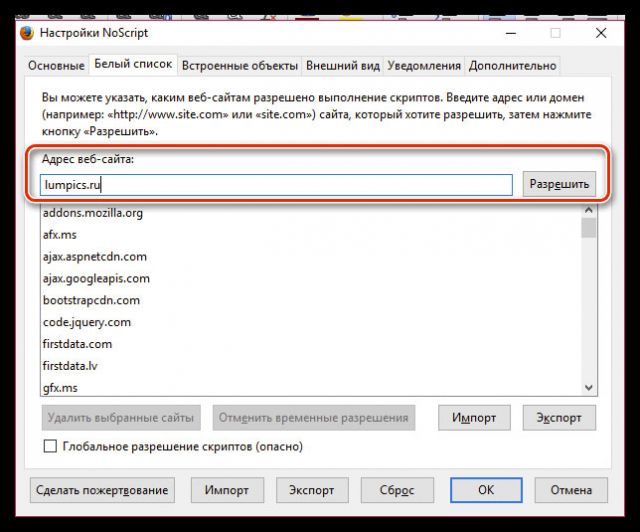
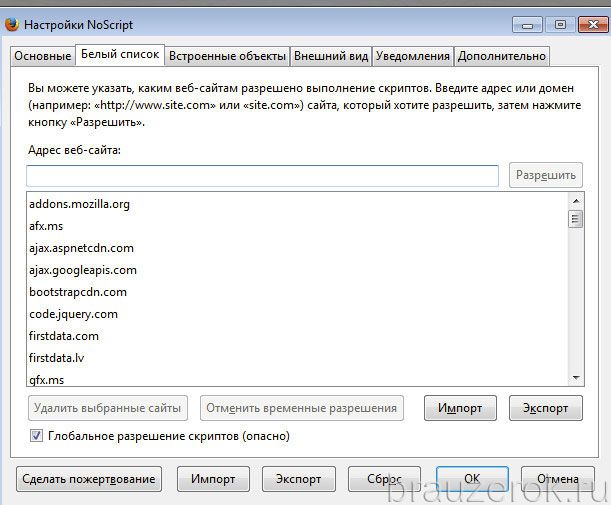
2.Переключитесь на раздел «Белый список». В строке введите адрес сайта. Нажмите на кнопку «Разрешить». Такую же процедуру проведите с остальными ресурсами.
После добавления сайтов в белый список вы получите возможность просматривать флеш-видео. Реклама, однако, вернется.
Привилегии ресурсов в закладках
Вы можете не создавать белый список в настройках NoScript, а включить параметр во вкладке «Основные» под названием «Разрешать выполнение JavaScript всем веб-сайтам из закладок». Что это означает? На сайтах, которые у вас сохранены в закладках, не будет работать расширение, то есть блокировка не будет производиться – все элементы с видео будут на месте.
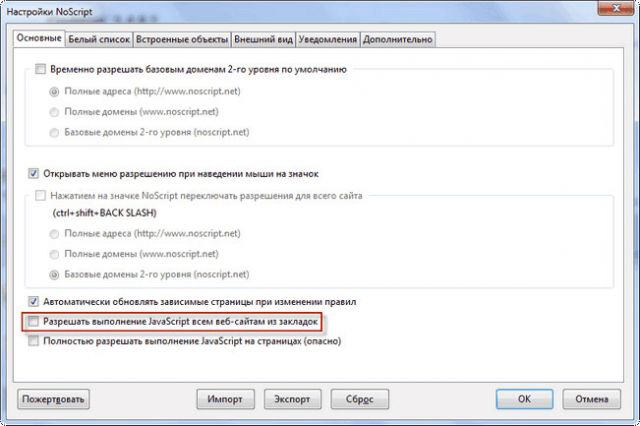
Таким образом, можно настраивать не список исключений, а свои закладки. Повод для его чистки: в них всегда накапливаются уже ненужные сайты. Единственный минус – отключаться будет только JavaScript. Все остальные плагины будут работать.
Другие настройки дополнения NoScript вы можете не изменять. По умолчанию стоят уже необходимые параметры.
Отключаем JavaScript без NoScript
Сам браузер позволяет выключать выполнение JavaScript и Java. Чтобы деактивировать JavaScript в Мозилла 23 и выше, следуйте инструкции ниже:
- В строке обозревателя, в которой пишут адреса сайтов, вбейте команду: about:config.
- В окне кликните по кнопке «Я обещаю, что буду осторожен!».
- В поисковом поле напишите javascript.enabled.
- Правой кнопкой мыши кликните по строке с состоянием по умолчанию и выберите параметр «Переключить».
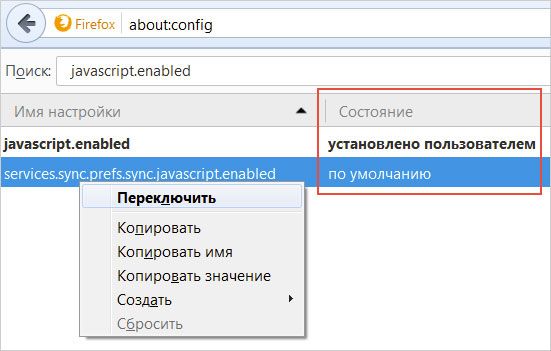
Если вы хотите активировать снова плагин JavaScript, поставьте первый параметр «установлено пользователем» обратно в этом же меню.
Для версии 22 и более старых вариантов предлагаем выполнить следующие шаги:
1.Заходим в раздел «Настройки».
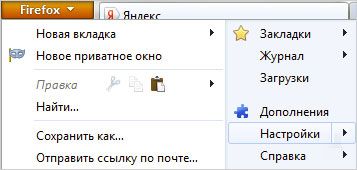
2.Переключаемся на третью вкладку «Содержимое» и снимаем отметку с пункта «Использовать JavaScript».
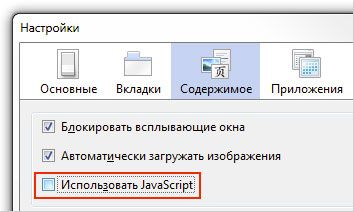
3.Кликните по ОК, чтобы изменения вступили в силу.
Отключаем Java без NoScript
Если вы вручную отключите плагин Java в настройках Firefox, Java-апплеты на страницах не будут запускаться тоже.
По умолчанию Firefox предлагает активировать Java, когда вы посещаете ресурсы с Java-содержанием. Что делаем для отключения?
- Кликните по иконке с тремя горизонтальными полосками и выберите пункт «Дополнения».
- Перейдите в раздел «Плагины».
- Кликните по Java(TM) Platform. Так, вы выделите плагин.
- В меню кликаем по кнопке «Никогда не включать».
Выключив эту функцию, пользователь избавит себя от постоянных предложений запустить Java.
Минус ручных отключений Java и JavaScript в том, что они производятся для всех страниц, открываемых в браузере. Нельзя с помощью инструментов Firefox отключить исполнение скриптов на конкретном веб-ресурсе.
Можно ли полностью отключить дополнение?
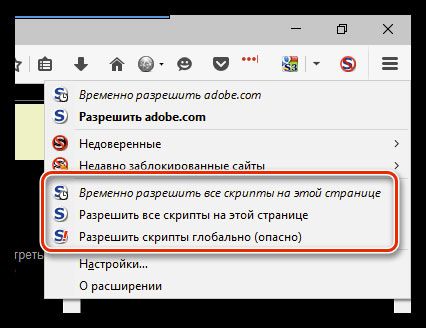
В меню самого расширения нет пункта «Отключить». Его можно найти в настройках браузерах в разделе «Расширения». Можно только разрешить скриптам работать на страницах временно или навсегда в пределах приложения. Будет три пункта:
- Временно разрешить все скрипты на этой страницы.
- Разрешить все скрипты на этой странице.
- Разрешить скрипты глобально.
Последний пункт разработчики крайне не рекомендуют активировать. Он отключит расширение для всех посещаемых вами сайтов.
Как удалить?
Если вам расширение больше не нужно, вы вправе его удалить из браузера. Это также своеобразный способ его отключения, так как вернуть дополнение можно в любой момент.
1.Зайдите в раздел «Дополнения» и переключитесь на вкладку «Расширения». В списке найдите NoScript.
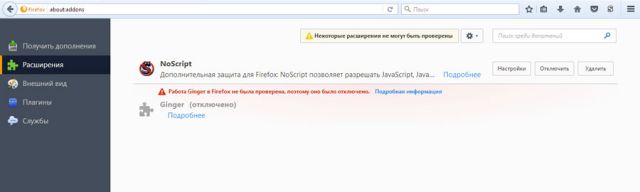
2.Нажмите на кнопку «Удалить». Если вы хотите выключить на время приложение, то кликните по «Отключить».
Это полезное дополнение для веб-обозревателя Mozilla Firefox. С ним серфинг по веб-ресурсам станет гораздо безопаснее. Вы избавитесь от назойливой рекламы. Недостаток его использования в том, что он будет также блокировать полезные вам элементы сайтов. Выход – отключать расширение на время на страницах или же создавать белый список для надежных сайтов, которые посещаете постоянно.
Как управлять JavaScript в Firefox

Модуль JavaScript в Firefox обрабатывает и запускает скрипты на веб-страницах, написанные на этом языке (одноимённое название): фреймы, интерактивные блоки, панели, анимационные эффекты, рекламные объявления, счётчики посещений и прочие аналитические инструменты.
Это руководство расскажет вам, как разрешить и как отключить JavaScript в браузере, какие плагины использовать для управления JavaScript в Mozilla.
Как выполняется отключение?
В последних версиях веб-обозревателя разработчики убрали опцию отключения/включения JS (сокращение — JavaScript) в настроечной визуальной панели. Деактивацию можно выполнить путём изменения параметров в скрытых настройках FF. Чтобы выполнить эту операцию, нужно:
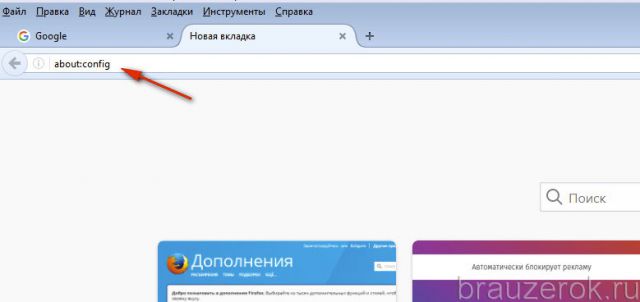
1. Набрать в адресной строке — about:config
А затем нажать «Enter».
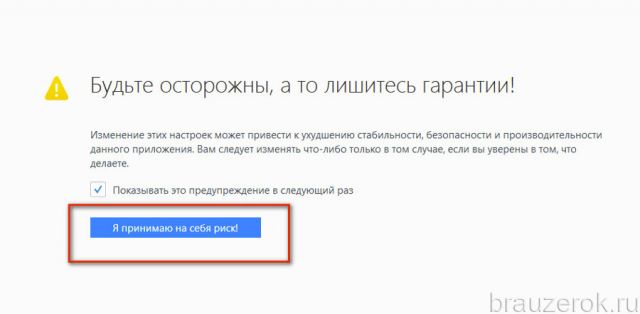
2. Под текстом предупреждения нажать «Я принимаю на себя риск!».
3. В поле поиск наберите — javascript.enabled
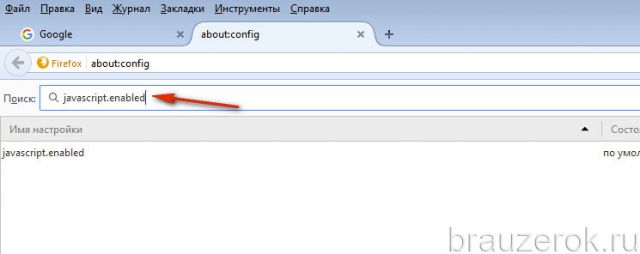
4. Клацните правой кнопкой по найденной функции (она отобразится в нижнем блоке «Имя настройки»). В контекстном меню запустите кликом мыши команду «Переключить».
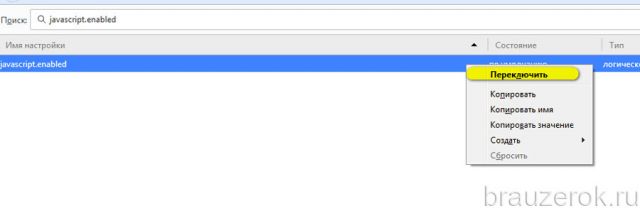
Значение функции поменяется с «true» на «false».
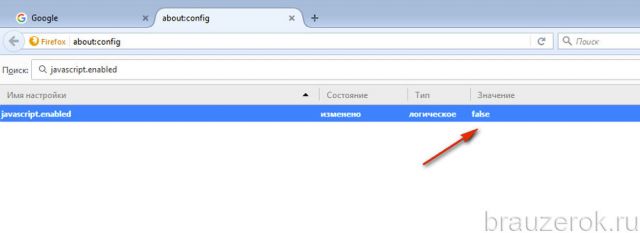
Совет! Быстро переключить настройку также можно двойным кликом левой кнопкой мыши.
После отключения все скрипты на веб-страничках функционировать не будут. Вернуть опцию в исходное положение (включить) можно аналогичным образом.
Аддоны
Дополнения позволяют создавать более гибкие настройки работы JavaScript, оперативно включать и отключать его. Рассмотрим популярные решения для управления JS.
NoScript
Продвинутый фильтр скриптов. Позволяет создавать чёрный и белый список JS по доменным именам. Предотвращает XSS-атаки, блокирует Clickjacking (скрытые ссылки и кнопки на элементах веб-разметки).
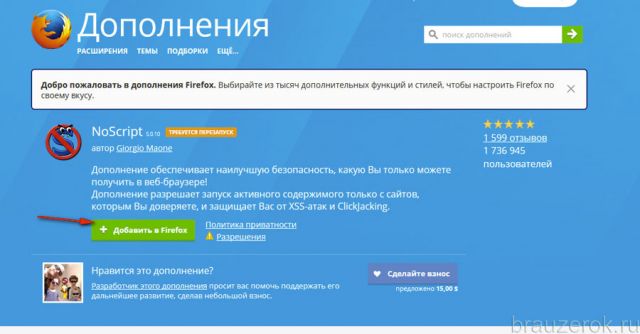
Чтобы настроить JavaScript на текущей вкладке, кликните иконку аддона (панель вверху слева). В списке кликом мыши присвойте статус «Недоверенный» скриптам, которые желаете отключить.
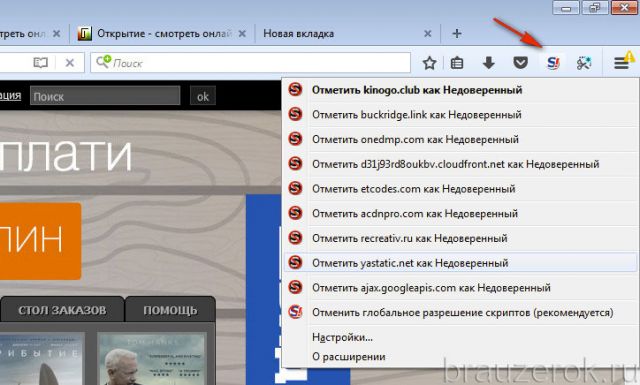
Команда в меню «Отменить глобальное разрешение… » блокирует все имеющиеся на странице объекты JS.
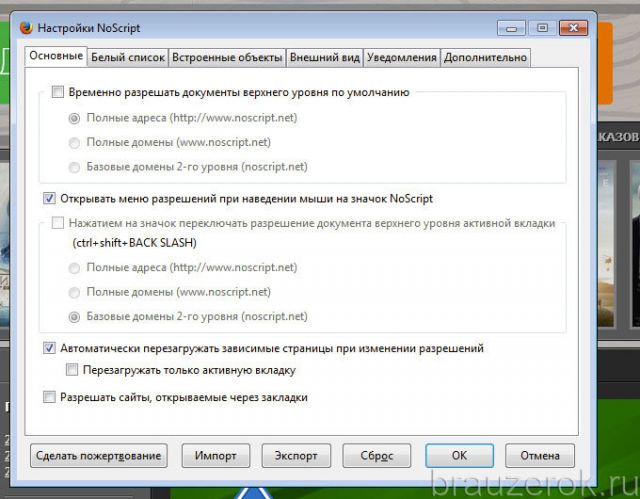
Чтобы перейти в настроечную панель расширения, клацните пункт «Настройки».
В окне опций, на вкладки «Основные», включается фильтрация по уровням, изменяются опции параметров управления.
«Белый список» — поле для добавления сайтов в исключения (на их страницах фильтрация аддоном выполняться не будет).
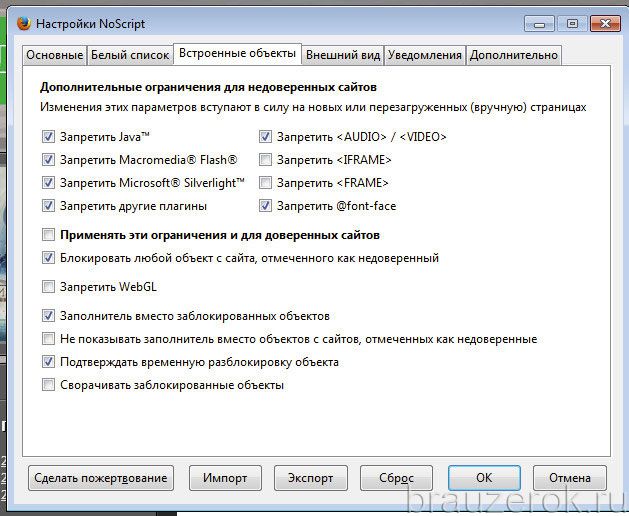
«Встроенные объекты» — включение/отключение запуска платформ Java, Flash, Silverlight, а также всевозможных фреймов.
«Дополнительно» — расширенные опции по обработке недоверенных доменов.
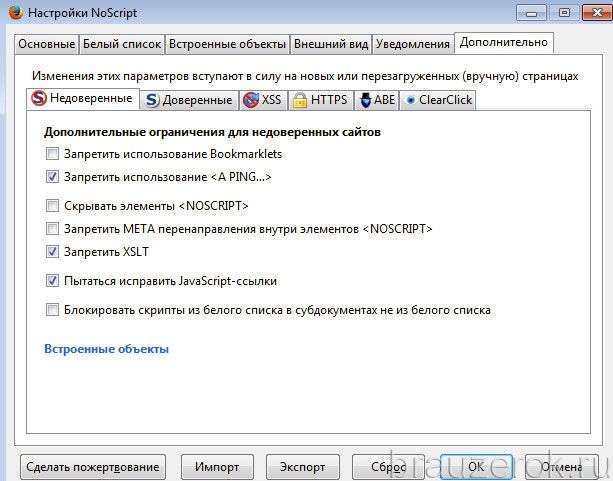
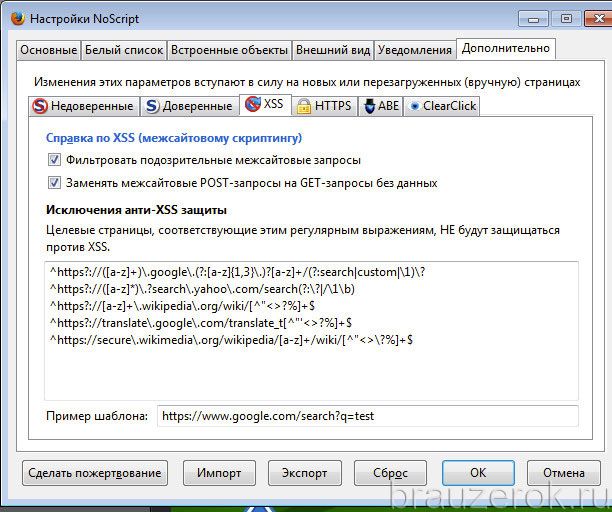
А также панель инструментов (XSS) для предотвращения вирусной атаки «межсайтовый скриптинг».
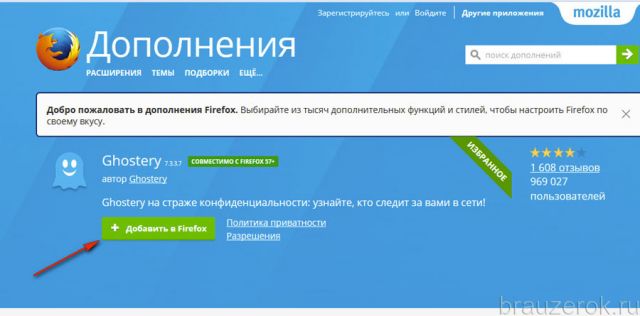
Ghostery
Выискивает и блокирует на сайтах потенциально опасные, сомнительные, нежелательные скрипты. А именно — баннеры, счётчики, «жучки», отслеживающие поведение посетителя на страницах сайта. Может быть использован в качестве антибаннера (блокировщика рекламы).
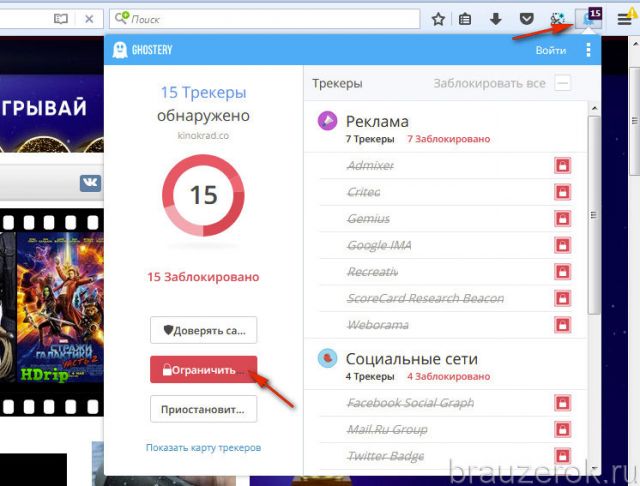
В панели расширения отображается статистика фильтра (сколько элементов было заблокировано) и типы обнаруженных функциональных блоков.
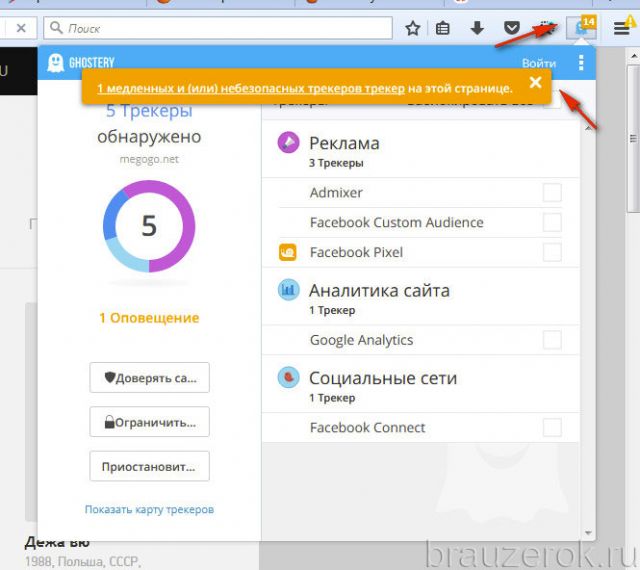
В левой части окна, под надписью «Оповещения», находится панель управления фильтра.
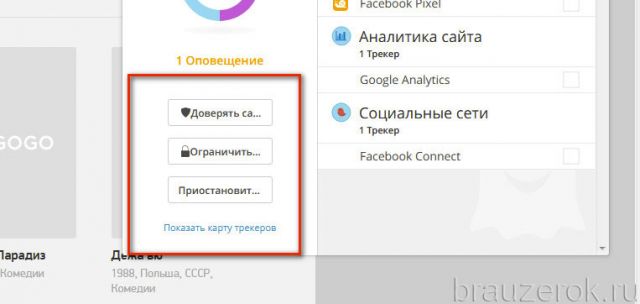
Кнопка «Ограничить» отключает все обнаруженные объекты. После её нажатия в строках трекеров появляется иконка «замок».
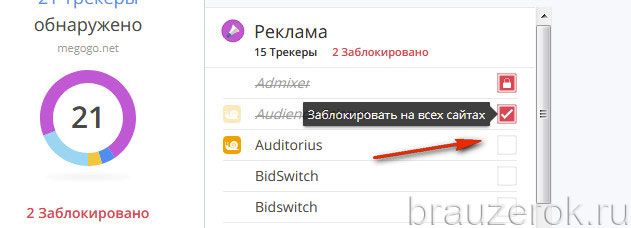
Чтобы отдельно отфильтровать какой-либо элемент, необходимо выбрать режим фильтрации непосредственно в его строке (например, кнопка «птичка» — активирует блокировку выбранного скрипта на всех сайтах).
QuickJava
Удобный, простой в пользовании фильтр, позволяющий одним кликом мышки активировать/деактивировать не только JavaScript, но и Flash, Java.
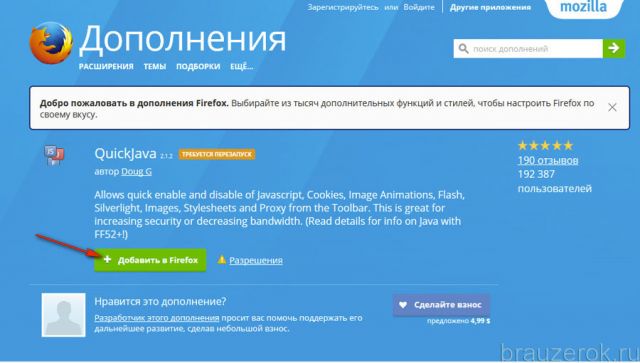
После подключения кликните его иконку. В ниспадающем меню щелчком мыши уберите «птичку» в строке JS.
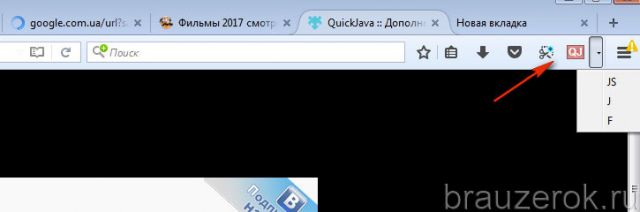
Обновите страницу, все элементы JavaScript исчезнут или же вместо них появится уведомление о том, что нужно включить модуль JS.
Активация скриптов также выполняется через меню расширения. Откройте его и кликом мышки установите в строке JS «птичку».
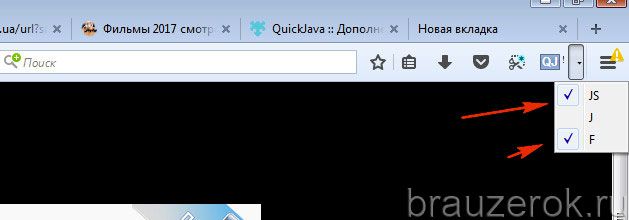
Примите во внимание то, что когда отключен JavaScript, отдельные страницы и сайты не могут полноценно функционировать. Например, на некоторых из них вы не сможете запустить аудио- или видеоплеер, поиграть в игру, открыть меню, отправить данные и т.д. Оптимальный вариант контроля над скриптами — настройка их фильтрации при помощи аддонов NoScript, Ghostery либо их аналогов.
NoScript Temporarily Disabled in Tor Browser
Note: This workaround should only be used temporarily, as it disables a security feature. Please remember to set the xpinstall . signatures . required entry back to true again once the Tor Browser security update is applied.
Sorry for the inconvenience.
Comments
Please note that the comment area below has been archived.
John (not verified) said:
Thanks for the workaround!…
Thanks for the workaround! Did it, it works fine so far. What exactly is the risk by setting it to false?
OT: Google captcha drives me crazy with Tor while surfing on many sites. It says my results are wrong and I have to do it again and again and again. 🙁 Is there a workaround? Thanks!
In reply to Thanks for the workaround!… by John (not verified)
Setting the pref to false…
So you should avoid installing new add-ons while this pref is set to false (installing add-ons in Tor Browser is generally not recommended anyway).
anon (not verified) said:
In reply to boklm
> installing add-ons in Tor…
> installing add-ons in Tor Browser is generally not recommended
Well. having less-trusted addons like NoScript preloaded in browser bundle sorta nullifies this recommendation. While some other addon can improve privacy even in private browsing environment and junk traffic thru tor circuits (which are slow already).
Anonymous (not verified) said:
In reply to > installing add-ons in Tor… by anon (not verified)
each noscript revision is…
each noscript revision is audited before it is included in the bundle.
anon (not verified) said:
In reply to each noscript revision is… by Anonymous (not verified)
Sure thing. Problem is that…
Sure thing. Problem is that NoScript receives updates thru addons.mozilla.org as well — as preconfigured in browser bundle effectively leaving an open sesame for any attack NoScript’s author wishes to perform again, see https://adblockplus.org/blog/attention-noscript-users
That’s why I don’t use NoScript at all (it is rather pointless in 2019 anyway).
Anonymous (not verified) said:
In reply to Sure thing. Problem is that… by anon (not verified)
No it’s not pointless in…
No it’s not pointless in 2019. I can still use something like 60-70% of websites with no js, and my lameass computer doesn’t lag as much.
Anonymous (not verified) said:
In reply to No it’s not pointless in… by Anonymous (not verified)
Me too.
Anonymous (not verified) said:
In reply to each noscript revision is… by Anonymous (not verified)
It’s a lie.
Anonymous (not verified) said:
In reply to each noscript revision is… by Anonymous (not verified)
Is it better to uncheck…
Is it better to uncheck update add-ons automatically?
Anonymous (not verified) said:
In reply to Is it better to uncheck… by Anonymous (not verified)
Yes. Autoupdate from…
Yes. Autoupdate from unverified sources is major security issue.
Anonymous (not verified) said:
In reply to Is it better to uncheck… by Anonymous (not verified)
It’s ok as long as you…
It’s ok as long as you remember to check (enable) it again after the patch is installed. Leaving automatic updates to add-ons turned off prevents automatic security updates to add-ons, so don’t leave it disabled for longer than it needs to be.
But it has no effect on the disabled status of NoScript.
Outraged user (not verified) said:
In reply to each noscript revision is… by Anonymous (not verified)
This happened WITHOUT…
This happened WITHOUT WARNING. The sudden disabling of NoScript resembles a ransomware assault. I interpreted this as corruption and I tried to re-install, and lost ALL my bookmarks! I have been digging but have no idea how or even if I can recover them.
This is OBSCENE.
Captain Hindsight (not verified) said:
In reply to This happened WITHOUT… by Outraged user (not verified)
There’s this little-known,…
There’s this little-known, super secret concept in IT, which allows to recover pretty much anything. It’s called a «Backup».
Lokapal (not verified) said:
In reply to There’s this little-known,… by Captain Hindsight (not verified)
In this case you should use…
In this case you should use TRUE time machine instead of «backup». Nothing has changed in Firefox/TOR/addons — internal certificates are just expired.
Anonymous (not verified) said:
In reply to In this case you should use… by Lokapal (not verified)
What is true time machine…
What is true time machine please?
Anonymous (not verified) said:
In reply to There’s this little-known,… by Captain Hindsight (not verified)
She didn’t think of backing…
She didn’t think of backing up but she’s right to be upset that it happened without warning.
Captain Gratitude (not verified) said:
In reply to There’s this little-known,… by Captain Hindsight (not verified)
Stop moaning you lame ass…
Stop moaning you lame ass moaners. You get this service for free. You act like 2 year olds some of you selfish, self centered candy ass moaners. Did it ever cross your self centered mind to say «hey Firefox/Tor, thank you for all the effort you put in to providing selfish moaning little nobody me with a free and usually pretty good and safe service.
Thank you Firefox/Tor workers for providing me a safe place on the Internet!
Anonymous (not verified) said:
In reply to Stop moaning you lame ass… by Captain Gratitude (not verified)
I agree that posters who are…
I agree that posters who are expressing harsh criticism of Tor devs or spreading FUD based upon misconceptions or misleading «spin» are not helping anyone, but I also feel that we all need to be sympathetic when something like this happens and some Tor users panic. After all, the most at-risk Tor users really might lose their freedom or even their life if a seriously bad entity is able to exploit some bug in the Tor ecosystem.
The good news in this story is that it seems the problem existed for only minutes to hours before Mozilla was notified, and Mozilla, Tor Project, and Tails Project all promptly issued fixes.
I would agree with anyone who says people who complain about TP should be making donations to help make things better, for example by allowing TP to become less reliant upon USG/Google.
MICIO (not verified) said:
In reply to This happened WITHOUT… by Outraged user (not verified)
You are right.
anon (not verified) said:
In reply to This happened WITHOUT… by Outraged user (not verified)
In the fact is was more…
In the fact is was more likely a TRIALWARE after time bomb went off.
Anonymous (not verified) said:
In reply to This happened WITHOUT… by Outraged user (not verified)
Bookmarks are stored in the…
Bookmarks are stored in the browser’s profile folder inside the tor-browser folder. They’re deleted if you delete the tor-browser folder. First, open your Recycle Bin. If they aren’t there, you need to immediately stop writing to the partition and scan it with forensic recovery software for deleted files. If you aren’t able to stop writing to the partition while your OS is running, plug the drive into another computer, and scan it from there, or scan it from a Live USB.
https://en.wikipedia.org/wiki/Data_recovery#List_of_data_recovery_softw…
Anon (not verified) said:
In reply to This happened WITHOUT… by Outraged user (not verified)
Поддерживаю! У меня в связи…
Поддерживаю! У меня в связи с этим тоже были опасения по поводу внезапного отключения всех дополнений в Tor Browser! Сначала копался в файлах так как полагал, что слетела система. Потом попробовал отключить проверку сертификата мозилла и дополнения появились в браузере и работали. Затем снова произошёл сбой! И тут я подумал, что поймал дикий вирус и система в полном ауте а я в полной жопе. Так и до инфаркта недалеко!
anonym (not verified) said:
In reply to > installing add-ons in Tor… by anon (not verified)
You don’t understand the…
You don’t understand the principle how torbrowser works.
If you ad Add-ons you change your Browser-fingerprint and loose your anonymity, cause you are a special snowflake in the mass of tor users.
Do you really think the tor project did not check noscript? Why do you use torbrowser if you do not trust them and think they are that stupid? If you think you understand the internet better than all the programmers, software-engineers and network-specialist at tor project, why don’t you build your own anonymous browser or network.
I am shocked every time to see how much people suffer from Dunning-Kruger-Effect.
anon (not verified) said:
In reply to You don’t understand the… by anonym (not verified)
> It’s a lie. > why don’t…
> It’s a lie.
> why don’t you build your own
Going to disregard kindergarten-tier exclamations, sorry.
> all the programmers, software-engineers and network-specialist at tor project
But let me remind you, what you are here on this page because one our trusted dependency been sloppy enough to lose the key (and, if you insist, the other our trusted dependency overlooked the flaw). This happened because such is life where sheet happens.
The case of NoScript is different because during that little war with Wladimir Palant, NoScript’s author INTENTIONALLY deployed the questionable updates (see the ABP blog link above). That’s why I’m treating NoScript addon as less-trusted and adding some entropy to my fingerprint having it disabled. Moreover, I have even more entropy from the use of uBlock Origin w/country specific lists for as partial replacement of NoScript functionality. I’d happily return back to line but not with NoScript, sorry, can’t make myself to trust it.
Anonymous (not verified) said:
In reply to > It’s a lie. > why don’t… by anon (not verified)
> Wladimir Palant You mean…
You mean the guy who charge companies for not blocking their ads? uBlock blocks everything without compromises and ransom-like schemes.
Anonymous (not verified) said:
In reply to > Wladimir Palant You mean… by Anonymous (not verified)
Was he disputing the fact he…
Was he disputing the fact he was charging them or just non-disclosing it?
Anonymous (not verified) said:
In reply to > It’s a lie. > why don’t… by anon (not verified)
@anon, you seem to know a…
@anon, you seem to know a lot about uBlock Origin.
Are you sure it doesn’t reveal your TRUE IP as some addons do? Or track you in some other way?
I see all the time that uBlock Origin sets a bunch of cookies every time it updates the Filter Lists from Easylist, Fanboy etc.
Anonymous (not verified) said:
In reply to You don’t understand the… by anonym (not verified)
What about themes? Do they…
What about themes? Do they change the browser fingerprint?
Anonymous (not verified) said:
In reply to boklm
Speaking of add-ons. I think…
Speaking of add-ons. I think there should be a preinstalled ad-blocker too. NoScript blocks ads as long as you don’t allow ANY scripts. Once you need to allow some scripts in order to make the website work correctly you’ll get the ads as well so if you don’t want ads you need to install at least an ad-blocker.
Anonymous (not verified) said:
In reply to Speaking of add-ons. I think… by Anonymous (not verified)
By blocking ads you are…
By blocking ads you are telling them something about yourself and making yourself stand out.
Anonymous (not verified) said:
In reply to By blocking ads you are… by Anonymous (not verified)
This wouldn’t be an issue if…
This wouldn’t be an issue if an adblocker was included by default with tor browser (and configured the same for all users). Tor browser users already stand out, the important thing is that you shouldn’t be able to tell one tor browser user from another.
cypherpunks (not verified) said:
In reply to Thanks for the workaround!… by John (not verified)
The suggested workaround is…
The suggested workaround is an UNEQUIVOCALLY BAD IDEA. WTF, disable signature checks? Never, never, never!
In the small picture, this is a real risk. In the big picture, Tor Project, are you deliberately training users to defeat «certificate validation» failed errors?
Good workaround: Open about:config and set javascript.enabled to false.
This will totally disable JavaScript. Therefore, NoScript is not needed. (Thanks to other cypherpunks in #30394.)
It may mess up the Security Slider, so this *after* setting the Slider to High. This way, you will also get settings such as disabling SVG, MathML, Web fonts. Or if you need JavaScript on some sites, set the Slider to Medium first (disables ultra-dangerous script features). Then, leave an about:config tab open so you can toggle JavaScript on and off.
(John, OT, Google is evil. Google, Cloudflare, et al. use soft coercion to make you abandon untrackable means of accessing the Internet. Don’t give in; just boycott affected sites as much as practical, and politely let their owners know why.)
Anonymous (not verified) said:
In reply to The suggested workaround is… by cypherpunks (not verified)
First, about:preferences…
First, about : preferences #privacy -> Permissions -> «Warn you when websites try to install add-ons» is enabled by default, and the only exceptions are to Mozilla-controlled first-party add-on websites. Mozilla vets the add-ons they list, and a user would have to visit Mozilla’s website, click the button on the page to install, and then see the warning that the browser displays and click on that. Difficult to do accidentally. Finally, the post makes very clear that the workaround should only be used temporarily (in bold) and reverted after the patch is installed. Disabling signature checks is not good, but there are many other layers of protection in place including telling users about the effects of the workaround and how to behave with it, so it isn’t as bad as you make it out to be.
Second, while disabling javascript will close many of the holes that were opened when NoScript was disabled, many users will need javascript enabled as you noted, but try explaining the intricacies of the relationship between the slider, NoScript, and Preferences to non-technical users and expecting them to know when to change what.
I agree on boycotting incessant captchas and pervasive Cloudflare, but many websites roll their own javascript or depend on relatively benign javascript frameworks to function. Disabling javascript disables all of them, not just Google and Cloudflare.
When the patch is released, its blog post and the next few that follow it should absolutely repeat the message to reset the preference back to True.
Anonymous (not verified) said:
In reply to First, about:preferences… by Anonymous (not verified)
Plus one.
Anonymous (not verified) said:
In reply to First, about:preferences… by Anonymous (not verified)
This is helpful. Thanks.
This is helpful. Thanks.
cypherpunks_lover (not verified) said:
In reply to The suggested workaround is… by cypherpunks (not verified)
This is the spirit! The…
This is the spirit!
The world will be a better place if we have more people like you and less like the one who recommend this sh**.
YOU ARE THE HERO, I LOVE YOU
Simple Rick (not verified) said:
In reply to This is the spirit! The… by cypherpunks_lover (not verified)
Is that supposed to be irony…
Is that supposed to be irony?
Or a case of «my girlfriend from Canada, you don’t know her»?
Sad in either case.
Anonymous (not verified) said:
In reply to The suggested workaround is… by cypherpunks (not verified)
I think the disabled…
I think the disabled signature checks are only for installing extensions. Unless you are installing extensions in Tor Browser (which is a bad idea), then it is totally harmless. It’s not like you’re disabling TLS PKI signature checks that are necessary for secure HTTPS sites.
Anonymous (not verified) said:
In reply to I think the disabled… by Anonymous (not verified)
That is a good point.
That is a good point.
Anonymous (not verified) said:
In reply to The suggested workaround is… by cypherpunks (not verified)
@ gk: Is cypherpunks right?…
Is cypherpunks right? Is disabling javascript that way s/he suggests a safer fix?
In reply to @ gk: Is cypherpunks right?… by Anonymous (not verified)
The safer fix is to wait for…
The safer fix is to wait for the update.
Anonymous (not verified) said:
In reply to boklm
Avoid web-surfing until the…
Avoid web-surfing until the fix is available? I am willing to try, but any idea when we can expect the fix? I know we depend upon Mozilla to fix the cause for NoScript breakage.
In reply to Avoid web-surfing until the… by Anonymous (not verified)
We now have a build that we…
We now have a build that we think is fixing the issue. If you want to help test it: https://people.torproject.org/~boklm/builds/8.0.9-build1/
We still need to sign it, do some QA and upload everything. If all goes well it should be released tomorrow (Monday).
Anonymous (not verified) said:
In reply to boklm
Thanks for the build! FTR,…
Thanks for the build! FTR, the above link is also available in onion: http://sbe5fi5cka5l3fqe.onion/~boklm/builds/8.0.9-build1/
I’ve visited sites that I commonly visited for 15 mins. Nothing bad seems to happen, except the tor button keeps blinking with an exclamation mark.
In reply to Thanks for the build! FTR,… by Anonymous (not verified)
The blinking is expected as…
The blinking is expected as the version is not releases yet (and, hence, not recommended).
Anonymous (not verified) said:
In reply to Thanks for the build! FTR,… by Anonymous (not verified)
Me too; the fix in 8.0.9…
Me too; the fix in 8.0.9 seems to be working fine for me.
In reply to boklm
It turns out the fix was not…
It turns out the fix was not complete, so we need to do a second build, delaying the release (probably until Tuesday): https://trac.torproject.org/projects/tor/ticket/30388#comment:39
Anonymous (not verified) said:
In reply to boklm
Does this mean that TB 8.0.9…
Does this mean that TB 8.0.9 and the latest Tails are not yet safe but still need to be fixed?
In reply to Does this mean that TB 8.0.9… by Anonymous (not verified)
8.0.9 includes the fix for…
8.0.9 includes the fix for this issue.
Anyway, even the previous version was still relatively «safe» if you were using the «standard» security level. It mostly made a difference for the users of the «safer» and «safest» security levels.
Anonymous (not verified) said:
In reply to boklm
Whew, OK, thanks, this…
Whew, OK, thanks, this thread has moved so quickly that it was a little hard to tell that 8.0.9 fixes the second issue which arose.
However, I use «safer» and «safest» almost exclusively.
Someone (not verified) said:
In reply to boklm
Not found
Anonymous (not verified) said:
In reply to The suggested workaround is… by cypherpunks (not verified)
>The suggested workaround is…
>The suggested workaround is an UNEQUIVOCALLY BAD IDEA. WTF, disable signature checks? Never, never, never!
Bad idea is mandatory signature verification for add-ons. If you can’t install add-ons without Mozilla’s permission — it’s not your browser. Mozilla add-on signature give a false sense of security.
Signed is NOT verified by Mozilla.
Mozilla removed today (August 16, 2018) 23 Firefox (signed) add-ons that snooped on users and sent data to remote servers, a Mozilla engineer has told Bleeping Computer today.
The list of blocked add-ons includes «Web Security,» a security-centric Firefox add-on with over 220,000 users, which was at the center of a controversy this week after it was caught sending users’ browsing histories to a server located in Germany.
«I did the investigation voluntarily last weekend after spotting Raymond Hill’s (gorhill) comment on Reddit, https://www.reddit.com/r/firefox/comments/96715s/make_your_firefox_brow… ,» Wu told us. «I audited the source code of the extension, using tools including my extension source viewer.»
«After getting a good view of the extension’s functionality, I used webextaware to retrieve all publicly available Firefox add-ons from addons.mozilla.org (AMO) and looked for similar patterns. Through this method, I found twenty add-ons that I subjected to an additional review, which can be put in two evenly sized groups based on their characteristics.
«The first group is similar to the Web Security add-on. At installation time, a request is sent to a remote server to fetch the URL of another server. Whenever a user navigates to a different location, the URL of the tab is sent to this remote server. This is not just a fire-and-forget request; responses in a specific format can activate remote code execution (RCE) functionality,» Wu said. «Fortunately, the extension authors made an implementation mistake in 7 out of 10 extensions (including Web Security), which prevents RCE from working.»
Anonymous (not verified) said:
In reply to >The suggested workaround is… by Anonymous (not verified)
But you can install addons…
But you can install addons without Mozilla’s permission, just not ones from addons.mozilla.org
common sense (not verified) said:
In reply to The suggested workaround is… by cypherpunks (not verified)
I consider signature checks…
I consider signature checks to be a to be a security vulnerability themselves if they disable security features like this. I don’t know how you think it’s helping anyway, being signed by Mozilla means almost nothing in the context of Tor Browser.
Anonymous (not verified) said:
In reply to Thanks for the workaround!… by John (not verified)
Cloudflare captcha? Go to…
Anonymous (not verified) said:
In reply to Thanks for the workaround!… by John (not verified)
> What exactly is the risk…
> What exactly is the risk by setting it to false?
If you forget to also disable autoupdates of addons, potentially a malicious attacker might be able to trick your browser into installing an (unsigned!) piece of malware masquerading as a legitimate update. Or if you forget and install an (unsigned!) add-on, you will have. installed unverified software, which again might be malware. It’s hard to guess how likely these scenarios really are, but the fact that they must be taken seriously because a certificate expired is really shocking and outrageous.
As I understand it, this emergency temporary mitigation is not a *fix* and it involves a security tradeoff.
o An intermediate cert needed to verify NoScript autoupdates expired owing to a goof at Mozilla.
o Ensuring that NoScript is working correctly is critical to Tor Browser.
o So you should disable signature verification until Mozilla fixes the cert.
o When that happens Tor Project will release an emergency new version of TB.
o Be careful to avoid installing any extension or allowing any autoupdates until the new TB is released; I think in most cases you should get a dialog box asking if you want to install something and of course you should say «No» because that something will not have been authenticated.
Anonymous (not verified) said:
In reply to > What exactly is the risk… by Anonymous (not verified)
> If you forget to also…
> If you forget to also disable autoupdates of addons, potentially a malicious attacker might be able to trick your browser into installing an (unsigned!) piece of malware masquerading as a legitimate update.
The bundled add-ons (HTTPS Everywhere and NoScript) update from mozilla.org by the preferences extensions . update . background . url and extensions . update . url in about : config [1]. So, if you don’t trust Mozilla’s review process for add-ons nor the developers of your add-ons, then you may want to temporarily disable automatic updates of add-ons. It’s a greater concern if you installed add-ons after installing Tor Browser. Mozilla probably is being extra cautious about reviewing add-ons or not doing it at all until most people install the patch.
How to disable automatic updates of add-ons:
Add-ons tab -> gear icon -> uncheck Update Add-ons Automatically. Or set extensions . update . autoUpdateDefault to False in about : config . It prevents your HTTPS Everywhere and NoScript from receiving security updates, so remember to enable it or set it to True again after you install the patch to be released for this bug.
In reply to > If you forget to also… by Anonymous (not verified)
We actually get HTTPS…
We actually get HTTPS-Everywhere from the EFF as we did not want to use the Mozilla version. That way in case Mozilla messes something up with their extensions we’d have at least HTTPS-Everywhere working as in this case.
Anonymous (not verified) said:
Very wise 🙂
Anonymous (not verified) said:
In reply to > What exactly is the risk… by Anonymous (not verified)
People must understand that…
People must understand that Signed != Verified
It’s exactly the same bullshit as signed programs in M$ Windows. It takes control from you and gives it to corporation (Mozilla Corp in this case), while giving you the false sense of security.
Anonymous (not verified) said:
In reply to People must understand that… by Anonymous (not verified)
+1 security minded people…
+1
security minded people are slow on this
Anonymous (not verified) said:
In reply to People must understand that… by Anonymous (not verified)
You have a point. But…
You have a point. But verifying a sig is much better than nothing, and TP needs to always bear in mind the possibility of overwhelming newcomers with esoteric concerns.
It’s a challenge, but we need to grow the Tor user base by leaps and bounds.
Anonymous (not verified) said:
In reply to Thanks for the workaround!… by John (not verified)
did this in the real firefox…
did this in the real firefox. the setting is there, but the addons in that browser remained disabled, and even after removal i couldnt redownload and install them with the workaround. i guess the same will be true for noscript: now its disabled the ff part of torbrowser will somehow know it was disabled unverified and prevent re-enable. cant reinstall. cant reenable. whats the point?
Anonymous (not verified) said:
In reply to did this in the real firefox… by Anonymous (not verified)
To take control from you of…
To take control from you of course, the same thing as with Windows 10 forced updates. It’s a corporate world. Use Waterfox of Palemoon, addons signing disabled there by default.
Anonymous (not verified) said:
In reply to Thanks for the workaround!… by John (not verified)
Supposedly using Chrome…
Supposedly using Chrome means getting less captcha challenges, so maybe changing user agent. Unless it’s some other magic behind the scenes data Chrome is telling google about you to tell recaptcha you’re real. Which I wouldn’t rule out.
Lisa (not verified) said:
In reply to Thanks for the workaround!… by John (not verified)
Google is just evil
Google is just evil
Anonymous (not verified) said:
In reply to Google is just evil by Lisa (not verified)
Don’t forget that Google is…
Don’t forget that Google is not just a company or an executive suite but also a large workforce of highly skilled employees, many of whom rebelled against Dragonfly (Censorbrowser) and Project Maven (the killbot death listing AI project for the Pentagon). Unfortunately those employees have already experienced retaliation. So we should direct our ire and the executive suite, not neccessarily people who work at Project Zero (for example).
Anonymous (not verified) said:
Is openly publishing for…
Is openly publishing for exit does still a good thing ? They become to easy blocked , tor is becoming heavily attacked more and more these days
Anonymous (not verified) said:
In reply to Is openly publishing for… by Anonymous (not verified)
I think it’s unavoidable…
I think it’s unavoidable. Exits go to the clearnet, so the clearnet can always see whether traffic from an IP looks like a proxy. If they weren’t published, third-party monitors would detect and list them as high traffic proxies anyway.
Anonymous (not verified) said:
In reply to Is openly publishing for… by Anonymous (not verified)
> Is openly publishing for…
> Is openly publishing for exit does still a good thing?
I don’t think there is any way of keeping the IPs of exit nodes secret. It is hard to even keep the IPs of bridges (unpublished «stealth» entry nodes needed for anti-censorship) secret.
Kim Jong-un sucks (not verified) said:
This is crazy dangerous and…
This is crazy dangerous and can have put peoples life on risk. Why can addons be disabled remotely anyway? This was not some kind of update where it stopped working after the user applied a update, but it just happened all by itself in the background. WTF! Tor devs you should not trust mozilla this much leaving this open channel, this proves why
Anonymous (not verified) said:
In reply to This is crazy dangerous and… by Kim Jong-un sucks (not verified)
True, this was a serious…
True, this was a serious blunder. But from what I understand, this happened because a certificate *expired*. If so, it wasn’t disabled remotely; it was disabled because a certain predetermined time had elapsed. It wasn’t a deliberate action from Mozilla or anyone else, and it wasn’t something that a malicious actor could have triggered if they had wanted to.
I hope that Tor Browser devs (and Mozilla too) will learn from this and make the system more robust in the future. Tor Browser should always trust the extensions that are bundled with it, and that trust shouldn’t be time-dependent. Ideally, it should also «fail closed» so that if NoScript is unavailable for any reason, the browser should default to javascript.enabled=false.
certifiable (not verified) said:
In reply to True, this was a serious… by Anonymous (not verified)
a certificate *expired*. …
a certificate *expired*.
Mozilla disabled another extension — not only noscript — in the regular firefox. if this fact pertains.
Anonymous (not verified) said:
In reply to True, this was a serious… by Anonymous (not verified)
> It wasn’t a deliberate…
> It wasn’t a deliberate action from Mozilla or anyone else, and it wasn’t something that a malicious actor could have triggered if they had wanted to.
Expiration can be deliberate, and actors can disrupt attempts to extend the time. Think of its relation to revocation too. But there aren’t indications at this point that this particular situation was deliberate.
Anonymous (not verified) said:
In reply to True, this was a serious… by Anonymous (not verified)
The problem also affected a…
The problem also affected a Mozilla FF-based browser extension serving to I2P base pack that installs. The error occurred in just the same moment.
anon (not verified) said:
In reply to True, this was a serious… by Anonymous (not verified)
Nothing is expired, they…
Nothing is expired, they have timer that checks signatures every 24 hrs, like in corporate gaming consoles, look for yourself here:
app.update.lastUpdateTime.addon-background-update-timer
app.update.lastUpdateTime.recipe-client-addon-run
services.blocklist.addons.checked
In reply to Nothing is expired, they… by anon (not verified)
The intermediate signing…
The intermediate signing certificate is expired which is why the extensions got disabled. Those timer checks are unrelated to that.
Anonymous (not verified) said:
In reply to This is crazy dangerous and… by Kim Jong-un sucks (not verified)
> Why can addons be disabled…
> Why can addons be disabled remotely anyway?
To verify the cryptographic signatures of code before installing an add-on, we need to verify the certs in a chain. In this case, one of those certs expired because Mozilla goofed. That silently disabled NoScript, putting us all at risk. Outrageous? Yes. Incredible? Unfortunately not, if you have followed decades of criticism of the many weaknesses of current PKI.
Security is hard. Very hard. This incident reminds us that human error remains as much a threat as malicious attacks exploiting some unrecognized technical flaw in software incorporated into the Tor ecosystem.
Anonymous (not verified) said:
In reply to > Why can addons be disabled… by Anonymous (not verified)
Another perspective: The sig…
Another perspective:
The sig files on the Tor Browser download webpage are a different type of cryptographic signature that we use to verify Tor Browser before installing it. They are created from Tor Project’s cryptographic keys that are also capable of having expiration dates. If those keys expire and we tried to verify the Tor Browser installer, we would either not be able to verify it or be presented with a warning message from our verifier program, i.e., gpg. But we wouldn’t be denied from installing it regardless or suddenly find it was uninstalled.
Anonymous (not verified) said:
In reply to Another perspective: The sig… by Anonymous (not verified)
Good point. But I would…
Good point. But I would never install unsigned code. Which unfortunately means I cannot help test alpha versions of some good stuff like upcoming Tails because (incredibly) these are unsigned.
Calbillie (not verified) said:
There is more to this and a…
There is more to this and a real solution will be for Tor to decouple from mozilla as much as possible. But really we need a new browser decoupled from all the states/govts and really if Tor doesn’t change then it becomes suspect in govt. chicanery.
Anonymous (not verified) said:
In reply to There is more to this and a… by Calbillie (not verified)
In an ideal world, clearly…
In an ideal world, clearly yes, Tor Browser should be independently developed with security in mind from the ground up, and regularly audited. That would take resources far beyond what TP will be able to muster in the foreseeable future.
I think the only long term solution, which satisfies among other desiderata the principle that «if you want it done right, do it yourself», is to evolve Tor Project from a tiny NGO dependent upon the «largesse» of untrustworthy governments and corporations to a user supported human rights NGO with a stupendous endowment enabling it to decline firmly offers of «help» :-p from the likes of Google, Amazon, Facebook, US State Dpt, DARPA, etc. That will take hard work, dedication, and a long-term commitment from community organizers, as well as a «no-strings» multimillion dollar gift to the Tor Foundation from some repentant tech billionaire.
Calbillie (not verified) said:
In reply to In an ideal world, clearly… by Anonymous (not verified)
Not an ideal world is…
Not an ideal world is required I’d say. Look at git. One guy started it (yes high visibility guy) and the ball started rolling. Why? Because it was clear to thoughtful people that it was the right thing to do. There are many thoughtful people that can see quite clearly that the current web trajectory is bad. We really have no choice but to create a new browser. What it’s based on? Don’t know.
Git is based on sound crypto science and the motivation of source freedom. And freedom from hindrances that alternatives had/have, technical/legal/etc.
So the right seed gets planted and right minded people will feel motivated to contribute. Otherwise it becomes yet another shitshow of which there are so many now (in all aspects of life).
Anonymous (not verified) said:
In reply to Not an ideal world is… by Calbillie (not verified)
So how do Tor Project and…
So how do Tor Project and ordinary users make something analogous happen for TP?
Anonymous (not verified) said:
After setting it to false…
After setting it to false restart Tor and then change it back to true so you won’t forget to later on. As long as you don’t restart again the addon still work for me fine though there is a warning about NoScript not being signed.
There is also another way to do this on Firefox though not Tor. Tools, Options, Privacy & Security, go to Browser Data Collection and allow Firefox to install and run studies. You can undo it right afterwards and it will still work.
Anonymous (not verified) said:
In reply to After setting it to false… by Anonymous (not verified)
Personally, I wouldn’t…
Personally, I wouldn’t enable studies before knowing what else it would do or install, but thanks for the info.
Anon (not verified) said:
@Calbillie What browser…
@Calbillie What browser would you use as the base of Tor? Better yet would you build an entire new one? Because that is an insane amount of work that will take a long time. This doesn’t even get into all the security checks that would need to be run by the community for quite a while before it would even be possible for download.
Then there would be porting over the addons over to the new browser, troubleshooting that until each work, make sure no security risks are added, etc.
Anonymous (not verified) said:
In reply to @Calbillie What browser… by Anon (not verified)
Chromium would be the…
Chromium would be the obvious choice. It’s a much more secure and stable base than Firefox, with a lot more resources behind it. Not sure how easy it would be to adapt it to the Tor Project’s needs though and to keep porting these changes to newer Chromium versions.
Anonymous (not verified) said:
In reply to Chromium would be the… by Anonymous (not verified)
Chromium-proper contains…
Chromium-proper contains Google integration.
Ungoogled-Chromium might be a better option?
Anonymous (not verified) said:
In reply to Chromium-proper contains… by Anonymous (not verified)
No, a hobby project by a…
No, a hobby project by a student is not a better option than Chromium.
Anonymous (not verified) said:
In reply to No, a hobby project by a… by Anonymous (not verified)
Something would have to be…
Something would have to be done about the integration.
Ungoogled-Chromium is not really a different/separate browser, it is just vanilla-Chromium gutted/patched to the extreme & updated per-release of vanilla-Chromium.
Other than being updated slightly faster, I fail to see how vanilla-Chromium is better in any way than Ungoogled-Chromium.
Anonymous (not verified) said:
In reply to Chromium would be the… by Anonymous (not verified)
The problem with Chromium is…
The problem with Chromium is that in effect you have to trust Google, a company which is reorganizing as part of the US military-surveillance complex (c.f. their AI kill-list for US drone strikes, to mention just the most notorious example). Or maybe even the CN military-surveillance complex (c.f. censorbrowser).
Yes, Chromium is open source, but is it really adequately audited on a continuing basis by reliable (non Google) coders? If not, Tor Project cannot possibly take on that job.
I have to agree with those who say that the only thing we can do is to urge Mozilla to try harder to avoid such dangerous (and embarassing) goofs in future.
Another advantage of Mozilla is that Tails is based on Debian which uses Firefox as the default browser. So there is a huge user base which has a stake in making Firefox safer.
Anonymous (not verified) said:
In reply to The problem with Chromium is… by Anonymous (not verified)
Mozilla needs to comply with…
Mozilla needs to comply with government requests just as Google does. Firefox also has Google integration, as well as its on trackers. You don’t have any privacy advantage if you compare stock Firefox to stock Chromium. All you have is a much weaker security model on Firefox.
Anonymous (not verified) said:
In reply to Mozilla needs to comply with… by Anonymous (not verified)
Mozilla has its issues, but…
Mozilla has its issues, but their corporate model appears to differ significantly from Google’s «All your life belong to us», which is just plain evil.
Anonymous (not verified) said:
In reply to Mozilla needs to comply with… by Anonymous (not verified)
Years ago I remember the…
Years ago I remember the precursor to Project Zero freaking out because they discovered a new and very dangerous APT attributed to CN military. In those days Google did not publicize USG state-sponsored malware, but reacted strongly to CN state-sponsored malware. They had cause to regret trusting USG when they read the Snowden leaks and saw that infamous smiley.
These days it appears possible, even likely, that Google is betting it can make more money by kow towinig to the CN dragnt surveillance machine than the US dragnet surveillance machine. If so in future you may see Google publicizing NSA APT malware but saying nothing about CN APTs.
Something to think about when you think about the meaning of the phrase «government requests».
Anonymous (not verified) said:
In reply to The problem with Chromium is… by Anonymous (not verified)
But Firefox is not safer. In…
But Firefox is not safer. In fact, it doesn’t even begin to compete with Chromium. There also isn’t a «huge user base» in Tails. The user base of Tor and Tails is so tiny, it would barely even show up on regular website analytics. Just because Firefox’s code is out there does not mean even one person just goes and audits it in their free time and keeps doing so for updated code. It’s just not what happens. It’s a fallacy to believe that just because something is open source, there will be people who audit its code. Google has a much better track record than Mozilla, when it comes to security. Security is an essential piece to even begin working on privacy. Firefox doesn’t offer it.
If you want something audited, you can pay a team of professionals to do so, and then keep doing so as the code is being changed. Nobody does it for free, for obvious reasons.
Anonymous (not verified) said:
In reply to But Firefox is not safer. In… by Anonymous (not verified)
> The user base of Tor and…
> The user base of Tor and Tails is so tiny, it would barely even show up on regular website analytics.
And we need to change that. Spread the word! Teach your friends to use Tor and Tails!
Anonymous (not verified) said:
In reply to Chromium would be the… by Anonymous (not verified)
Chromium’s a bad choice due…
Chromium’s a bad choice due to reasons detailed in the past (not sure how relevant these issues still are perhaps someone should take another look?):
Anonymous (not verified) said:
In reply to Chromium’s a bad choice due… by Anonymous (not verified)
Chromium might be a bad…
Chromium might be a bad choice for what the Tor Project wants to accomplish, but Firefox is a horrible foundation. It’s just objectively much worse in terms of security.
Anonymous (not verified) said:
In reply to Chromium’s a bad choice due… by Anonymous (not verified)
And besides all those…
And besides all those reasons, Chromium’s main developer is a company that’s business model is built on ads and therefore «sharing» user data with other parties, and any decisions they make will be a compromise between real security and their bottom line, which is essentially built on breaking privacy.
Anonymous (not verified) said:
In reply to Chromium’s a bad choice due… by Anonymous (not verified)
If I remember correctly, the…
If I remember correctly, the issue with Chromium wasn’t so much that you’d have to make all this changes. After all, many changes had to be made to Firefox too. Rather, Chromium not accepting changes upstream was the issue and having all this patches rebased onto every release is error prone and time intensive. Probably not doable with the small team working on Tor Browser at all. Mozilla, however, accepts patches to upstream Firefox and is even willing to help with advice, review and making sure the features keep working.
Anonymous (not verified) said:
In reply to Chromium would be the… by Anonymous (not verified)
Yeah let’s turn the web into…
Yeah let’s turn the web into a Chromium monopoly.
Woza (not verified) said:
In reply to Yeah let’s turn the web into… by Anonymous (not verified)
Lets use an insecure browser…
Lets use an insecure browser, because «muh free market economics».
The Chromium code base originated in the open source code community, while Firefox is commercial code that comes from the company that made the Netscape browser. Google doesn’t own Chromium, it belongs to the world.
Anonymous (not verified) said:
In reply to Lets use an insecure browser… by Woza (not verified)
I remember when Netscape was…
I remember when Netscape was the cool new kid on the block.
I don’t think you are accurately recounting the history.
Anonymous (not verified) said:
In reply to Yeah let’s turn the web into… by Anonymous (not verified)
I highly doubt the…
I highly doubt the completely negligible market share of people using the Tor Browser would have any impact on that.
Anonymous (not verified) said:
In reply to Chromium would be the… by Anonymous (not verified)
Does anyone really think…
Does anyone really think Google’s going to backport security or anti-tracking stuff from a Tor Chromium to mainline Chromium? Because Firefox does. For example:
https://www.zdnet.com/article/firefox-to-add-tor-browser-anti-fingerpri…
Or just search for «Tor Uplift», the Firefox project to review and integrate privacy changes from Tor into Firefox master.
Barry (not verified) said:
Weird. My Tor Browser (8.0.8…
Weird. My Tor Browser (8.0.8) and its default plugins (NoScript 10.6.1, HTTPSEverywhere 2019.1.31 are working without issue and it’s showing that I’m running the latest version.
Is this blog post in relation to non-default plugins only?
Blazito (not verified) said:
In reply to Weird. My Tor Browser (8.0.8… by Barry (not verified)
I’m on default plugins…
I’m on default plugins. HTTPS everywhere is working but NoScript is disabled.
Barry (not verified) said:
In reply to Weird. My Tor Browser (8.0.8… by Barry (not verified)
Disregard my post above!…
Disregard my post above! NoScript suddenly stopped working on my 8.0.8. Apologies
Testing. (not verified) said:
In reply to Weird. My Tor Browser (8.0.8… by Barry (not verified)
» Weird. My Tor Browser (8.0…
» Weird. My Tor Browser (8.0.8) and its default plugins . are working without issue «
Is your system-clock set correctly ??
Blazito (not verified) said:
Has anyone been able to get…
Has anyone been able to get NoScript working? The work around posted does not work for me. Regular firefox has been fixed for me and all the addons are now working, but TOR still has NoScript disabled. Is TOR going to push an update?
somebody (not verified) said:
In reply to Has anyone been able to get… by Blazito (not verified)
After setting xpinstall…
After setting xpinstall.signatures.required to FALSE in about:config it worked for me.
Anonymous (not verified) said:
In reply to Has anyone been able to get… by Blazito (not verified)
Yes, the workaround worked…
Yes, the workaround worked for me. The NoScript icon came back on the toolbar some minutes after I set the preference to false, and I didn’t restart. See if it comes back after you close and restart the browser.
Anonymous (not verified) said:
In reply to Has anyone been able to get… by Blazito (not verified)
>The work around posted does…
>The work around posted does not work for me
After you change the about:config preference «xpinstall.signatures.required» from Value «true» to Value «false», you have to quit and restart Tor Browser.
mehdi (not verified) said:
SHAME ON MOZILLA! What…
SHAME ON MOZILLA!
What happened with prenty of already installed add-ons which suddenly got remotely deactivated by Mozilla (no choice given to the user about what to do) is UNACCEPTABLE and INEXCUSABLE since it unexpectedly left Tor Browser users exposed, without security feautres they were trusting and using in that moment to protect their privacy: a rogue move by Mozilla that could have possibly pose threat to the lives of activists and dissenters whose presence in the world wide web relies on Tor Browser. The Mozilla Foundation and those in charge of the Firefox development roadmap must be held accountable for their misconduct. Plain and simple: they acted as miscreants. Was it only a matter of carelessness?
It’s extremely sad to state that the Mozilla Foundation seems to be increasingly focused on its own politically biased agenda: more propaganda and far less technological care, respect and responsibility towards its user base.
I call on the steering group of Tor developers: please take seriously into account the incident of such sudden deactivation of (critical) Firefox add-ons, including those bundled with Tor Browser!
Firefox is an UNRELIABLE piece of software to build privacy upon. The Mozilla Foundation is an UNRELIABLE and TREASONOUS partner. Seriously, look for a viable alternative!
eh (not verified) said:
In reply to SHAME ON MOZILLA! What… by mehdi (not verified)
If you happen to come back…
If you happen to come back to check replies, please state any conflicts of interest you may have in writing this comment such as:
- if you receive any money from a competitor that could benefit from Mozilla’s loss
- if you receive money or participate in a consumer protection organization that could benefit from maligning Mozilla
- if you have had a dispute with Mozilla in the past that hasn’t been satisfactorily resolved.
as you do not seem to be looking at this situation objectively.
costa (not verified) said:
In reply to If you happen to come back… by eh (not verified)
I think that risking one’s…
I think that risking one’s freedom or one’s life is a sufficient reason, it is not necessary to assume any conflict of interests.
This is not (only) a usability problem and it is not even a 0-day worth a million dollar, this is a very serious problem caused by an equally serious carelessness from the mozilla team.
Anonymous (not verified) said:
In reply to If you happen to come back… by eh (not verified)
javascript can now be…
javascript can now be covertly used to find the real ip address of dissidents. but this is now apparently unobjective. i would point out that whether or not this is the law of unintended consequences biting torproject in the ass before mozilla, i would say thats irrelevant. the fact remains that because of firefox devs making a poorly judged decision, and then brute forcing it on people rather than giving a warning and offering them the choice whether to take a judgement call on the risk on their addons, that peoples real lives are now at risk, more than they would have been had they not had tor at all.
no i have no connection to mozilla or any browser maker. i actually prefer firefox over chrome because i find ff easier to deal with in terms of addons, finding and using them. chrome can be quite opaque in its features also.
but while i used both, i no longer trust firefox, because of the FORCED nature of its decision. and because tor did not seemingly know about it.
its going to be a while if this gets on the mainstream news, and longer if anyone dies because of it, for mozilla to recover. if it doesnt wind up going under.
In reply to javascript can now be… by Anonymous (not verified)
Just to reply to your first…
Just to reply to your first point: No, there is no known way to recover the IP address in Tor Browser just by JavaScript being enabled. Not sure if you meant something else, though.
Anonymous (not verified) said:
In reply to javascript can now be… by Anonymous (not verified)
> rather than giving a…
> rather than giving a warning and offering them the choice
Mandatory signing was controversial when it was introduced in 2015. Speaking of warnings, there was «a transition period of two release cycles (12 weeks total) during which unsigned extensions [only generated] a warning in Firefox. After the transition period, it [was not] possible to install unsigned extensions in Release or Beta versions of Firefox.»
https://blog.mozilla.org/addons/2015/02/10/extension-signing-safer-expe…
https://blog.mozilla.org/addons/2015/04/15/the-case-for-extension-signi…
https://wiki.mozilla.org/Add-ons/Extension_Signing
Anonymous (not verified) said:
In reply to SHAME ON MOZILLA! What… by mehdi (not verified)
It’s not the first incident…
It’s not the first incident. And it will be ignored by Tor developers as usual. Relax.
Anonymous (not verified) said:
In reply to It’s not the first incident… by Anonymous (not verified)
Ignored by tor developers?…
Ignored by tor developers? You realize you’re commenting on a Tor blog post that is dedicated to addressing this specific issue? They gave a workaround and said they will ship a fix when it is available from Mozilla. What else do you want?
Anonymous (not verified) said:
In reply to It’s not the first incident… by Anonymous (not verified)
yes, you are absolutly right…
yes, you are absolutly right! that’s the biggest fail.
Anonymous (not verified) said:
In reply to It’s not the first incident… by Anonymous (not verified)
I’m unsure what you mean by…
I’m unsure what you mean by ignoring. It’s only a handful of people working on Tor Browser, and yet there is already this blog post, the necessary changes to the code have been made and the fixed version is already being built and tested. Seems pretty good to me.
Of course, it would be better if more people helped out. Perhaps, then the next issue like this is discovered and fixed even before the certificate expires.
Anonymous (not verified) said:
In reply to I’m unsure what you mean by… by Anonymous (not verified)
> fixed even before the…
> fixed even before the certificate expires.
A few ideas have been posted as Trac tickets. For instance, #30394 and #30402. The larger Firefox community is probably coming up with many more ideas.
Anonymous (not verified) said:
In reply to SHAME ON MOZILLA! What… by mehdi (not verified)
> The Mozilla Foundation and…
> The Mozilla Foundation and those in charge of the Firefox development roadmap must be held accountable for their misconduct. Plain and simple: they acted as miscreants.
Mozilla has been doing a great job at improving privacy for their users lately. There is Firefox Focus, implementation of containers, accepting patches for Tor Browser (investing a considerable amount of their own time on advice and review), matching donations to Tor and much, much more.
Do you really want to blame Mozilla? To me, I’d seem they are doing a better job at security and privacy than almost all of organizations on the internet. Also, it rather odd to blame someone for trying to do the right things.
> Was it only a matter of carelessness?
Are you suggesting this could have been intentional? If so, with what purpose?
> Seriously, look for a viable alternative!
Is there one? Please let me know.
Anonymous (not verified) said:
In reply to > The Mozilla Foundation and… by Anonymous (not verified)
Yup, Mozilla’s documentation…
Yup, Mozilla’s documentation references Tor Browser as an inspiration for containers.
Anonymous (not verified) said:
In reply to SHAME ON MOZILLA! What… by mehdi (not verified)
> Was it only a matter of…
> Was it only a matter of carelessness?
The fact that the inadvertent logic bomb detonated a few days *after* May Day is indirect but useful evidence that this was not a deliberate act engineered by «the usual suspects» (e.g. FBI). Because the usual suspects would likely want to spy on Tor users just *prior* to May Day not just *after* May Day.
More importantly, over the years there have been a number of widely reported new stories about some huge company forgetting to update a cert. So there’s plenty of evidence that organizations large and small are finding it very difficult to maintain their cryptographic assets.
I don’t mean we should excuse Mozilla (or anyone else) from overlooking a critical deadline; my point is that there is no reason (AFAIK) to think this was anything other than a mistake. A serious mistake, but a mistake which to their credit Mozilla quickly fixed.
Anomous (not verified) said:
In reply to SHAME ON MOZILLA! What… by mehdi (not verified)
Sadly, I must agree with the…
Sadly, I must agree with the final assessment. Though FireFox/Mozilla has, over time, come to be trusted, the excuse that it doesn’t allow such add-ons as NoScript due to cert failure, simply doesn’t hold water. As the base, which controls cert behavior and setting the handshake needed for validation, FireFox does not require a specific cert to be incorporated w/in their Add-on suite and therefore, restrictions to the HTTPS/NoScript add-ons should not have that excuse used (overlooking cert validation) when they fail to permit an Add-On.
In most cases, the reasoning the general public hears, is not true. There are multiple channels that can be used to ensure that a specific event does or does not happen, and something that has been a stable capability for years is not suddenly affected.
Developers for both FireFox/TOR and other Mozilla based products in most occasions follow one simple rule: If it’s not broken, don’t fix it. This spans across any organization which must fund their resources based on time-spent towards a specific Goal and Objectives. That funding can only occur if there is sufficient money to use in order to make enhancements and/or platform changes.
By blocking and preventing key components from being installed and used, especially for those that have been around for as long as NoScript has, this change was conscious and intentional, with the target for what this add-on offered to the public.
And, while the Organization shall find a so-called «workaround» or eventually permit the originally branded product to be used, this entire approach to suddenly remove its ability from the platform did nothing but buy some time for the platform developers to devise a side-step to what shall eventually be permitted.
Make no mistake about it. There are people w/in Mozilla and elsewhere that expect anything based on this technology to follow requirements, otherwise, funding shall be stripped, and failure to comply shall result in unpleasant and personally impact consequences for all stakeholders in the product and product supply chain.
It is a sad day folks. Your privacy and all aspects surrounding your public and private life can and is likely to be impacted. Not only in free countries, but around the globe where others tend to simply make someone disappear when they don’t think they want what they’re doing to stay with them.
mainland (not verified) said:
Some people had it disabled…
Some people had it disabled about 10 UTC and some 20 UTC. On what it depends?
Anonymous (not verified) said:
In reply to Some people had it disabled… by mainland (not verified)
Signatures of add-ons are…
Signatures of add-ons are checked in Firefox’s code whenever something calls XPIDatabase . verifySignatures ( ) or possibly XPIInstall . verifySignedStateForRoot . A timer is hard-coded to call verifySignatures ( ) every 24 hours after you open the browser, but other actions may call it at any time. I was unable to search for «verifySignatures» to find all actions that call it on Mozilla’s web repository because the search timed out, and I didn’t want to clone the whole repository just to search for a string. I don’t know if Mozilla’s hotfixes verify them immediately or how long it waits.
Blazito (not verified) said:
Reinstalling TOR does not…
Reinstalling TOR does not solve the issue either. I guess we’re waiting on a small update.
Anonymous (not verified) said:
In reply to Reinstalling TOR does not… by Blazito (not verified)
You can reinstall Tor and do…
You can reinstall Tor and do not wait for the Mozilla’s «solution» using the following workaround:
. Browser\TorBrowser\Data\Browser\profile.default\user.js
########################
# User Preferences
user_pref(«app.update.auto», false);
user_pref(«app.update.enabled», false);
user_pref(«extensions.update.enabled», false);
user_pref(«extensions.update.autoUpdateDefault», false);
########################
So you have to
1) install fresh Tor
2) +remove checkbox «start TBB» at the ending of installation. (do not start TBB.
)
3) put user.js to the «profile.default» folder
4) now you can start TBB easy — it will work
It helps with Windows TBB. BTW when Mozilla&TBB will solve the issue — you HAVE to change all «false» to «true» certainly.
Anonymous (not verified) said:
In reply to Reinstalling TOR does not… by Blazito (not verified)
installed an old version of…
installed an old version of tor browser with updates off and it has no script.
Anonymous (not verified) said:
In reply to installed an old version of… by Anonymous (not verified)
Old versions are susceptible…
Old versions are just as susceptible and have more unpatched vulnerabilities. I don’t know if your method of turning off updates has any effect on checking signatures, but if it does, it wouldn’t work unless you turned it off very quickly before it ran the automatic routines.
Nib (not verified) said:
Thanks for the info and hard…
Thanks for the info and hard work. Good luck!
Wally (not verified) said:
I have been hoping that Tor…
I have been hoping that Tor Project would move from Firefox to a Chrome based browser, after Theo de Raadt said Chromes security is better.
Anonymous (not verified) said:
In reply to I have been hoping that Tor… by Wally (not verified)
what and have WebRTC leaks?…
what and have WebRTC leaks? no thanks
Anon (not verified) said:
In reply to I have been hoping that Tor… by Wally (not verified)
DO NOT ever use Google…
DO NOT ever use Google products that call home like a Chrome based browser!
Wally (not verified) said:
In reply to DO NOT ever use Google… by Anon (not verified)
So you use a version with…
So you use a version with the commercial spy stuff removed.
Interesting comment about the two code bases here:
«There’s a great irony here…
Firefox is a derivative of the Mozilla code base which used to be known
in the general public as Netscape. Netscape Communications was a
for-profit company, that actually *sold* their browser for commercial
use (it was only free for personal use).
Chrome and Safari both derive from Apple WebKit which itself is a fork
of the KHTML rendering engine developed by the KDE project, and has
*always* been, LGPL licensed code since its first release in 1998.
Yet today, Firefox is held up as the open-source darling and
Chrome/Safari is seen as the proprietary devil. Go figure. :-)»
Anonymous (not verified) said:
In reply to DO NOT ever use Google… by Anon (not verified)
[b]TBB is phoning home too…
[b]TBB is phoning home too. this cert check on every launch. maybe there’s more we don’t know. [/b]
In reply to [b]TBB is phoning home too… by Anonymous (not verified)
That cert check that broke…
That cert check that broke is done *locally*. Otherwise it would have been easy for Mozilla to unbreak all the disabled extensions.
Anonymous (not verified) said:
In reply to I have been hoping that Tor… by Wally (not verified)
I disagree. It’s true that…
I disagree. It’s true that google has the resource to employ world-class security researchers in the world (google project zero discovered numerous security bugs) to make their browser secure.
However, privacy-wise (which is Tor Browser all about!), chrome is a very poor choice. One has to understand that making profit with user’s data is part of google’s business model, e.g, gmail scans user’s mail for targeted advertisement. Chrome is especially bad, it is a chromium (which is free/libre and open-source) based proprietary browser with many anti-privacy features (such as sending your usage pattern to google).
Being proprietary, it is impossible to audit the code. Even if we choose to base tor browser on chromium instead of chrome, it would be a maintenance nightmare to make absolutely sure all anti-privacy features has been turned off in chromium.
A better option is to use a non-corporate-backed browser — which is firefox!
If you want firefox to be more secure, please help to report bugs or denote!
Anonymous (not verified) said:
In reply to I disagree. It’s true that… by Anonymous (not verified)
See also comments further up.
Wecker 2 (not verified) said:
In reply to I have been hoping that Tor… by Wally (not verified)
Chromium NOT Chrome …
Chromium NOT Chrome . BIG difference
Anonymous (not verified) said:
In reply to I have been hoping that Tor… by Wally (not verified)
You’re crazy.
Anonymous (not verified) said:
In reply to I have been hoping that Tor… by Wally (not verified)
Chrome (well, Chromium,…
Chrome (well, Chromium, which is the open source version) is significantly better. I’m an exploit dev, so I’m not just parroting what someone else said! Chromium has more and better security mitigations that make traditional exploits very hard to use and necessitate complex and unreliable exploit chains. Firefox is much easier to exploit. The only benefit Firefox had over Chromium, which was the power of the XUL browser extension API, no longer exists now that WebExtensions are a thing and now NoScript in Firefox is not nearly as powerful as it used to be.
Unfortunately the real reason Tor Project can’t move to Chromium is that Firefox is easier to maintain a fork of because it releases snapshot versions called «ESR». Chromium is much harder to track and requires a bigger and more dedicated team to manage, even if it is more secure.
Simple Rick (not verified) said:
In reply to Chrome (well, Chromium,… by Anonymous (not verified)
«I’m an exploit dev, so I’m…
«I’m an exploit dev, so I’m not just parroting what someone else said!»
We don’t know that.
Anonymous (not verified) said:
In reply to «I’m an exploit dev, so I’m… by Simple Rick (not verified)
No, but it’s all too…
No, but it’s all too plausible that NSA/TAO, GRU, and other state sponsored hackers regularly read Tor dev lists, monitor Tor dev chat rooms, and even occasionally post in this blog.
It’s also plausible that such entities have tried, are trying, and will continue to try to insert their own operatives into TP as a kind of «double agent». I hope that TP is trying hard to make that difficult.
Anonymous (not verified) said:
In reply to «I’m an exploit dev, so I’m… by Simple Rick (not verified)
You’re right, you just have…
You’re right, you just have to trust me. It doesn’t really matter though anyway because it’s not that elite of a position. I’m not one of those experts with a dozen priceless 0days in his home dir.
Anonymous (not verified) said:
In reply to Chrome (well, Chromium,… by Anonymous (not verified)
I suppose one shouldn’t ask…
I suppose one shouldn’t ask for whom you develop exploits or what your intentions are.
That aside, I think you have correctly explained why currently TP really has no viable alternative to being based upon Firefox ESR.
Anonymous (not verified) said:
In reply to I suppose one shouldn’t ask… by Anonymous (not verified)
I think it’s a fine thing to…
I think it’s a fine thing to ask. Answer: I develop exploits because it’s fun and lets me root personal devices that otherwise would be locked down («jailbreaking»), because I hate DRM and I hate that a device you own is not truly yours. When I find bugs in software that people rely on (e.g. browsers, OS components) I contact the vendor and disclose the vulnerability used so that they can fix it. I am not an exploit broker who sells bugs, and I despise people and companies which do.
An exploit dev is not automatically a black hat who sells their bugs!
Anonymous (not verified) said:
In reply to I have been hoping that Tor… by Wally (not verified)
You need to look at the long…
You need to look at the long-term part: which browser is actively rewriting core parts of its browser into a memory safe language (Rust)? (Stylo, WebRender, .. more are coming)
Anonymous (not verified) said:
More information about this…
null (not verified) said:
Firefox is dead since their…
Firefox is dead since their intentional ridding of ALSA as a fallback audio interface in Linux, their sly attempt at adverts as a browser and these incidents.
Palemoon Browser needs more publicity. if the team behind Palemoon and Tor worked together at making Palemoon «secure» and the default Tor browser, that would be perfect.
retrojedi (not verified) said:
In reply to Firefox is dead since their… by null (not verified)
Yes, Pale Moon is the bloat…
Yes, Pale Moon is the bloat-free, lightweight version (fork) of Firefox, i love it too. It would be optimal for Tor. And — if privacy — don’t trust Google-related products.
Reading it on Pale Moon at the moment 🙂
No thanks (not verified) said:
This wasn’t a «mistake» …
This wasn’t a «mistake»
This was intentional to get users to share data
Judge Judy (not verified) said:
In reply to This wasn’t a «mistake» … by No thanks (not verified)
Prove it.
No thanks (not verified) said:
In reply to Prove it. by Judge Judy (not verified)
prove what? you must be…
prove what? you must be ignorant. if you think Google and Facebook are spying on you but Mozilla isn’t you must be brainwashed.
1. this isn’t the first time Mozilla slipped into this mess, do you like Mr. Robot because Firefox knows you do.
2. check out the steps needed for a temp fix.
3. your browser just REMOTELY disabled something without your permission. no alarm bells are ringing in your head? . have you checked the source to see if anything else can be remotely controlled?
DancingTatanka… (not verified) said:
In reply to prove what? you must be… by No thanks (not verified)
Hey that thought came(?) to…
Hey that thought came(?) to my mind as well. how was it disabled without me doing anything?
But we should believe someone sometimes, just to make ourselves feel better.
Somebody else (not verified) said:
In reply to prove what? you must be… by No thanks (not verified)
Nothing we know indicates…
Nothing we know indicates this particular event, the expiration of an intermediary PKI certificate, was intentional.
Name (not verified) said:
In reply to prove what? you must be… by No thanks (not verified)
What is even more funny,…
What is even more funny, they became bold and push for remote controlled «hotfix» in the «studies» — literally the thing that let’s them control your browser remotely 24/7. If you disable that, you wont receive the «hotfix» — corporate fear tactics.
Anonymous (not verified) said:
In reply to Prove it. by Judge Judy (not verified)
He’s correct.
Anonymous (not verified) said:
In reply to He’s correct. by Anonymous (not verified)
Prove it.
Philip Manzur (not verified) said:
Hi friends. having noticed…
Hi friends. having noticed that Java Script is still enabled despite using (as always) the highest level in my settings, I would like to know whether you recommend to stop using Tor till the problem is finally solved. sorry for my simple question, but I am a «newbie» in technical matters. Thank you very much indeed for all your efforts and permanent support. best regards.
In reply to Hi friends. having noticed… by Philip Manzur (not verified)
Yes, not using Tor Browser…
Yes, not using Tor Browser during one or two days until the update fixing this is available can be an option. The other option is the workaround mentioned in the blog post.
Philip Mansur. (not verified) said:
In reply to boklm
Thank you very much for your…
Thank you very much for your answer.
Anon (not verified) said:
DO NOT ever use in TOR a…
DO NOT ever use in TOR a Chrome based browser which is made by Google and spy on you!
Anonymous (not verified) said:
In reply to DO NOT ever use in TOR a… by Anon (not verified)
Don’t worry, there is no…
Don’t worry, there is no chance TP will ever adopt Chrome (or even Chromium probably) as the basis for «Tor Browser gen 2».
Adding security features after the fact as Mozilla tries to do with FF is not the best way, but currently it may be the best way TP can actually use.
To get a specialty browser writtten ground up for TP you need to give TP a LOT of money.
certifiable (not verified) said:
warning. mozilla disabled…
warning.
mozilla disabled noscript extension, leaving javascript enabled
set this to «false».
about:config?filter=javascript.enabled
also, when mozilla auto-disables an extension, they should automatically set associated Firefox prefs to the secure value.
is this mozilla «bug worthy»?
Anonymous (not verified) said:
In reply to warning. mozilla disabled… by certifiable (not verified)
I’m confident that patches…
I’m confident that patches in the near future will make it fail closed, not open as it did.
unsure (not verified) said:
blunder of the decade. but…
blunder of the decade. but sure, let’s keep firefox as our frontend, just toogle this boolean and that boolean and then toogle it again. :poolparty:
tor needs something simple like epiphany, midori or falcon.
Anonymous (not verified) said:
In reply to blunder of the decade. but… by unsure (not verified)
In general, simplicity is…
In general, simplicity is better for security, but many users would complain if TP adopted a new browser which simply does not allow complex risky things like watching videos.
John (not verified) said:
Chrome is belong to Google…
Chrome is belong to Google and Google Secretly Spying with Chrome.
RB (not verified) said:
Shame on you! Don’t even…
Shame on you!
Don’t even think about using Chrome with the tor project. Google Chrome — Spyware
smallDetails (not verified) said:
Has anyone noticed that The…
Has anyone noticed that The Tor Project has been open and honest about this problem ?
Anyone notice that posts critical of The Tor Project have remained ?
Sometimes its the little things.
Anonymous (not verified) said:
In reply to Has anyone noticed that The… by smallDetails (not verified)
Plus one.
Anonymous (not verified) said:
In reply to Has anyone noticed that The… by smallDetails (not verified)
You should see the comments…
Anonymous (not verified) said:
Mozilla is working on a fix,…
Mozilla is working on a fix, and we’ll start building a new Tor Browser version as soon as their fix is available.
Don’t forget Tor 0.4.0.5!
In reply to Mozilla is working on a fix,… by Anonymous (not verified)
0.4.0.5 won’t be included in…
0.4.0.5 won’t be included in this update, as we try to minimize unrelated changes to avoid issues which would delay the update. We also did not test the dormant feature introduced in 0.4.0.5 in an alpha yet, so it will probably get included in the next alpha first.
Anonymous (not verified) said:
In reply to boklm
Very wise under the…
Very wise under the circumstances.
Anonymous (not verified) said:
During this time, malicious…
During this time, malicious actors are likely to take advantage of the fact that many people do not read this blog. This is a big deal and puts into question trust in Mozilla.
Anonymous (not verified) said:
In reply to During this time, malicious… by Anonymous (not verified)
Take advantage in what way?…
Take advantage in what way? It’s basically the same as moving the security slider to «low» isn’t it? If someone was going to take advantage, for example by a javascript exploit, wouldn’t they have been doing so all along? I guess there could be a greater number of tor users now with JS enabled and thus more potential victims, but.
It’s not like it was silently disabled. The browser gives you a big yellow banner the moment NoScript is disabled. If you moved the security slider above its default «low» in the first place, than you should have a pretty good idea of what that warning means and the implications of it. If you choose to go on using the browser without NoScript, and you choose not to check the Tor blog for news about the issue, then it kind of becomes your own fault.
It’s like ignoring your check engine light and then blaming the manufacturer when your car finally breaks down.
Anonymous (not verified) said:
In reply to Take advantage in what way?… by Anonymous (not verified)
> Take advantage in what way…
> Take advantage in what way? It’s basically the same as moving the security slider to «low» isn’t it?
For most users who were (only briefly we hope) affected, that is probably right.
The problem is that the higher settings of the security slider offer substantial security improvements which might really be needed by some users for some things, and (for a short time) some of them might not have realized that NoScript had been disabled which broke the higher settings.
Right now there appears to be no reason to think the cert expiration was deliberate (it is well known that large organizations have a lot of trouble avoiding this kind of mistake entirely) so there is reason to hope that adversaries such as NSA were caught flat footed just like we were, and were unable to quickly exploit the problem to attack us. We hope.
Anonymous (not verified) said:
In reply to During this time, malicious… by Anonymous (not verified)
IKR? The old website had…
IKR? The old website had the blog post titles on the front page.
Anonymous (not verified) said:
In addition to disabling a…
In addition to disabling a security feature, does this change the browser fingerprint at all? Wouldn’t this workaround significantly increase the attack surface in the browser? Why is Tor Browser «phoning home» to Mozilla anyways? I’m not a cybersecurity expert nor do I pretend to be, I am genuinely curious.
Anonymous (not verified) said:
In reply to In addition to disabling a… by Anonymous (not verified)
xpinstall.signatures…
xpinstall . signatures . required doesn’t change the browser’s fingerprint. Add-ons, for one thing, do. By setting it to false and making sure NoScript comes back, your fingerprint will go back to looking like Tor Browser as long as you don’t install or manually disable add-ons. Tor Browser updates its privacy-security add-ons from Mozilla’s repository and works with add-ons as Firefox. Tor Project works with the developers of the add-ons it bundles and audits their source code. But it’s definitely good to look into the extent of what’s phoning Mozilla and if it’s necessary.
name (not verified) said:
In reply to In addition to disabling a… by Anonymous (not verified)
Because Tor developers made…
Because Tor developers made stupid decision to move from 52 ESR to corporate controlled 60. This is direct and expected conclusion for that.
Anonymous (not verified) said:
In reply to Because Tor developers made… by name (not verified)
Minus one. Tor devs often…
Tor devs often face tough choices to be made in a short time with imperfect information. On the whole I think they tend to make the best possible choices under often difficult circumstances.
I think we probably agree that in an ideal world, security/privacy/anonymity would not be so hard. And I hope you agree that we can get closer to the ideal if we can move Tor Project to a user supported funding model and greatly increase its operating budget, free of government/corporate influence. I hope you will consider making a donation to TP.
(I am a user like you, not an employee of TP.)
Serge (not verified) said:
The hotfix is available here…
Anonymous (not verified) said:
Georg Koppen, why do you, as…
Georg Koppen, why do you, as the only one decision-making person, publish this inconvenient blog post about forcing users to manually switch off the security feature in order to make Tor Browser to operate properly instead of doing an emergency release with NoScript added to sig verification exceptions as Torbutton?
In reply to Georg Koppen, why do you, as… by Anonymous (not verified)
We are currently working on…
We are currently working on an update, but this cannot be done instantly. Meanwhile, we have this short blog post (which was also reviewed by a few people) to explain the issue and give a possible workaround for the people that can’t wait for the update.
Anonymous (not verified) said:
In reply to Georg Koppen, why do you, as… by Anonymous (not verified)
1. In part, because I (a Tor…
1. In part, because I (a Tor user) asked him to do so (in the #tor chat room).
2. Mostly because keeping Tor users informed about critical security issues is obviously an absolutely appropriate thing to do.
Also, the problem is that Mozilla goofed by letting a certificate expire, which had the horrible effect of silently disabling NoScript, an essential part of TB security. So TP needs to wait for Mozilla to fix the cert before TP can issue an emergency bug fix for TB.
Thanks again for posting!
Anonymous (not verified) said:
In reply to Georg Koppen, why do you, as… by Anonymous (not verified)
> NoScript added to sig…
> NoScript added to sig verification exceptions as Torbutton
Hey, that’s a good idea. extensions . legacy . exceptions Easy for developers, transparent to users, and if I understand correctly has the same effect as xpinstall . signatures . required but precise to NoScript, not all add-ons.
In reply to > NoScript added to sig… by Anonymous (not verified)
Yes, that’s one of the…
Yes, that’s one of the options on the table. However, this kind of exception has the risk that there might be holes open now to get you a non-signed malicious NoScript installed. So, there is a trade-off to make here as well.
Anonymous (not verified) said:
On regular firefox it’s …
On regular firefox it’s «fixed» by allowing Firefox to install and run studies
Lisa (not verified) said:
OMG, not having no script…
OMG, not having no script really sucks. I was ad-free at a spot I visit often. Now, I’m getting one ad after another. I hope whatever this problem is, it can be solved. I feel like I’m under attack.
Joe (not verified) said:
The workaround isn’t working…
The workaround isn’t working in regular Fx 63. Changing «xpinstall.signatures.required
to false & restarting Fx doesn’t reverse disabling of addons.
Maybe forcing Fx to check for addon updates AFTER the about:config change is needed for the fix to work? In regular Firefox I did a manual check for addon updates — were none.
Restarted Fx — no change.
However, in regular Fx following Mozilla’s suggestion of enabling «Studies» in Fx preferences, here: https://blog.mozilla.org/addons/2019/05/04/update-regarding-add-ons-in-…
& restarting Fx, then waiting a couple of minutes — doing another check for addons & all addons were enabled again.
They mention it might take much longer (hours) for the Studies to be applied in Fx and also some different, associated issues some users reported (& list possible fixes) .
Anonymous (not verified) said:
@ gk: Thanks for the blog…
Thanks for the blog post!
Anon (not verified) said:
The real fix to this would…
The real fix to this would be to develop on the Gnome or KDE browsers instead.
If people keep using chromium or firefox as bases they will inevitably keep breaking features and by extension users privacy and security. I’m sure quite a few peoples password security will be at risk right now as well.
Firefox has been slowly feature creeping to a standard that the big tech companies want: more cloud features, more 3rd party extension, and less data actually kept securely in the hands of their actual users.
At least with a project like Gnome you’d know there’d be an army of other linux users waiting to fork the browser if there was any issues like this.
Anonymous (not verified) said:
One important point no-one…
One important point no-one is talking about: when did the cert expire and when did Mozilla learn about the problem?
If this was an unrecognized critical flaw for many months that would change this from «a serious blunder which could potentially endanger people all over the world» to «a serious blunder which likely cost an unknowable number of political dissidents their lives or freedom».
In reply to One important point no-one… by Anonymous (not verified)
Mozilla says they learned…
Anonymous (not verified) said:
In reply to boklm
Thank you, every bit of…
Thank you, every bit of information helps. What I really need to know now is when the certificate which caused the problem actually expired.
Note for anyone following the link, the «fix» they describe does not apply to Firefox ESR, which will be fixed «soon».
Anonymous (not verified) said:
In reply to Thank you, every bit of… by Anonymous (not verified)
> when did the cert expire…
> when did the cert expire and when did Mozilla learn about the problem?
Expired:
Sat May 4 00:09:46 2019 UTC (2019-05-04)
Mozilla bug #1548973 reported:
Sat May 4 00:49:00 2019 UTC (2019-05-04)
About 39 minutes after it expired.
«Some reports on reddit says that they had their clocks a day forward, but they may be just early canaries for the actual widespread issue.» [1]
It’s a PKCS #7 certificate. [2] Certificate information:
Or do it yourself:
- Copy the NoScript add-on installer (XPI file) from your Tor Browser folder to a temporary folder so you can work on it. The XPI file is named as the UUID of NoScript: 73a6fe31 — 595d — 460b — a920 — fcc0f8843232 (See question 2.6 in NoScript FAQ. Microsoft calls them GUID’s.) ./ tor — browser_en — US / Browser / TorBrowser / Data / Browser / profile . default / extensions / { 73a6fe31 — 595d — 460b — a920 — fcc0f8843232 } . xpi
- XPI files are ZIP files, so open it in your local unzip program. If it returns errors, rename the XPI file to something normal like noscript . xpi .
- Extract the mozilla . rsa file. ./ META — INF / mozilla . rsa
- If you have openssl command line tools installed, open a terminal (command line prompt), cd to the folder containing the extracted mozilla . rsa , and type this command: openssl pkcs7 — in mozilla . rsa — inform der — print [4]
You can grep just the names, dates, and times by doing:
openssl pkcs7 — in mozilla . rsa — inform der — print | grep — B1 — A3 — i valid
> the «fix» they describe does not apply to Firefox ESR, which will be fixed «soon».
«A Firefox release has been pushed. version 60.6.2 for ESR.» (Sun May 5 20:25:00 2019 UTC (2019-05-05)) [5]
Anonymous (not verified) said:
In reply to > when did the cert expire… by Anonymous (not verified)
Thanks for the information…
Thanks for the information about when the cert expired.
Anonymous (not verified) said:
In reply to > when did the cert expire… by Anonymous (not verified)
> XPI files are ZIP files,…
> XPI files are ZIP files, so open it in your local unzip program.
unzip had a bug which was recently fixed in Debian.
Don’t know how much to worry about that; my point is that we all need to be careful to avoid making things worse with an ill-conceived «fix».
Anonymous (not verified) said:
In reply to One important point no-one… by Anonymous (not verified)
From what I read this cert…
From what I read this cert should have auto updated. Believe that post was on reddit and if true its not looking good for Tor.
Anonymous (not verified) said:
In reply to One important point no-one… by Anonymous (not verified)
> If this was an…
> If this was an unrecognized critical flaw for many months.
When a cert is created, the «before» and «after» dates are displayed or manually entered. Whoever made it was told the date when it would expire. It was very likely recognized. But it was forgotten, neglected, or ignored. The cert was valid from 2017-05-04 to 2019-05-04 which implies that it was created and recognized(!) on 2017-05-04 or sometime between that range of dates for it to have been of any usefulness.
anon (not verified) said:
Please ensure core addons…
Please ensure core addons cannot be disabled in the future for whatever reason, I was wondering why javascript was working despite being on the safest security level
Anonymous (not verified) said:
In reply to Please ensure core addons… by anon (not verified)
this easy thing is still not…
this easy thing is still not obvious for tbb-team, unfortunately.
Anonymous (not verified) said:
In reply to Please ensure core addons… by anon (not verified)
> for whatever reason…
> for whatever reason
Including if the user intentionally disables or removes them?
clueless (not verified) said:
So to be clear, setting …
So to be clear, setting «xpinstall.signatures.requiredentry» to «false» only effects installing addons ? Is there any other effects this will have? Is this just for getting noscript to work again? What does no script do that disabling javascript doesn’t?
Anonymous (not verified) said:
In reply to So to be clear, setting … by clueless (not verified)
Many websites require at…
Many websites require at least some scripts to be allowed in order to work properly. With NoScript you can decide which scripts you allow. With disabling javascript it’s all or nothing. If you want to make a website to work you need to enable javascript and then you let in ALL scripts. Not just the ones that are needed to make the website work.
Suggestions (not verified) said:
Some alternative browsers…
Some alternative browsers have been suggested in this thread and on other sites.
Browsers like Waterfox, Pale Moon, Vivaldi, Brave.
I would prefer the comparatively lesser known Icecat browser.
I like their user centric approach to privacy.
Desktop: www.gnu.org/software/gnuzilla/
Android: f-droid.org/en/packages/org.gnu.icecat
Hanol (not verified) said:
Thank a lot for the tip.
Thank a lot for the tip.
PLAS (not verified) said:
For those who know, it’s…
For those who know, it’s safer to disable Javascript from about: config or have noscript give extra protection?
Anonymous (not verified) said:
In reply to For those who know, it’s… by PLAS (not verified)
Of those two, xpinstall…
Of those two, xpinstall restores the browser fingerprint of the slider settings and NoScript’s ability to manage the disabling of JavaScript.
another user (not verified) said:
This problem seems like a…
This problem seems like a simple enough oversight, especially as the advice has always been to not to install add-ons. The real mistake imo is that TBB’s Security Level functionality depends on an add-on (NoScript), which in turn is dependent on externalities out of Tor Project’s control/purview.
Functionality integral to Tor Browser should be integrated into Tor Browser: In this case that would mean building NoScript functionality into Tor Browser rather than continuing to employ it as an add-on. Please look into making this happen in a future release.
In reply to This problem seems like a… by another user (not verified)
Yes, that’s another option…
Yes, that’s another option on the table we could pick and not an unreasonable one (even though it will require quite some engineering effort). We’ll discuss it once the dust has settled a bit.
AGNUnymous (not verified) said:
While Chromium seems more…
While Chromium seems more secure to some people, as it probably contains more security features the following also needs to be taken into account:
— The source code is very hard to audit. It is for instance hard to make sure that Chromium is free software, or even to make sure that it’s legal to redistribute as this bug report shows: https://bugs.chromium.org/p/chromium/issues/detail?id=28291.
— Security is very dependent on the threat model. For Apple, the people using some of their products (Iphones and Ipads) are a threat. But for many people used by Apple’s products, Apple’s tight control over the device that they bought and use is a threat. So for the latter, Apple’s security (restricted boot which forces people to be used by their operating system, and denying users right to install the applications they want without Apple’s consent) is a very serious threat. So having that security broken or having no such security is crucial for people’s freedom privacy and security. As I understand Firefox’s threat model is way more aligned to the tor-browser’s threat model than Chromium’s.
— As I understand, more generally speaking, the Firefox political goals are more aligned with the tor-browser’s political than Chrome’s. As such, the design decisions and the code written carry out that political goals. As the tor-browser relies on upstream codebases for various reasons, it’s probably more practical to help improve Firefox’s security by working with them, rather than trying to retrofit privacy and freedom into a project like Chromium that might be driven by totally incompatible and antagonist objectives. It might also not be a very good idea to spend an enormous amount of resources just to keep up developing and maintaining that privacy and freedom retrofitting as the new versions of Chromium are released. Spending that amount of resources in a way that is more sustainable and has greater long term impact would be wiser. It would also have greater political impact as it could make the organizations that develop free software browsers better, and more generally try to influence web standards to respect users freedom and privacy and try to empower users as much as possible.
Anonymous (not verified) said:
In reply to While Chromium seems more… by AGNUnymous (not verified)
Plus one.
Concerned (not verified) said:
I agree with previous…
I agree with previous comments, even if Mozilla stays oblivious TOR really needs to have some means of avoiding things like that in the future
rrkdl (not verified) said:
thx anyway for the temporary…
thx anyway for the temporary fix .. )
Gob (not verified) said:
To put it simply. Tor…
To put it simply. Tor browser is no longer safe as scripts cant be blocked but the so called work around also causes security problems. Are we supposed to just not use tor until this is fixed? It seems like the most obvious question to me.
Anonymous (not verified) said:
In reply to To put it simply. Tor… by Gob (not verified)
The security problem caused…
The security problem caused by workaround is a problem only if you want to install add-ons because now there’s nothing to tell if they are safe or not. So after the workaround you can use Tor just fine. Just don’t install any add-ons.
aegir (not verified) said:
Thanks guys
kurosh (not verified) said:
I am waiting for newest…
I am waiting for newest update or smallupdate for this problem.
more thanks for your tries.
Anonymous (not verified) said:
Add a message on the TBB…
Add a message on the TBB download pages and/or remove the TBB download links. Echoing ticket #30402.
anon (not verified) said:
How is this still broken? It…
How is this still broken? It has been over 40 hours. Get your shit together, seriously!
name (not verified) said:
In reply to How is this still broken? It… by anon (not verified)
Use the Waterfox.
Use the Waterfox.
Micio (not verified) said:
In reply to Use the Waterfox. by name (not verified)
No bad at all
Anonymous (not verified) said:
In reply to How is this still broken? It… by anon (not verified)
That’s really constructive,…
That’s really constructive, way to be a team player.
In reply to How is this still broken? It… by anon (not verified)
Well, to begin with Mozilla…
Well, to begin with Mozilla took way longer than usual to provide a fix and they needed several trials to get this right as this is more complicated than it looks. Additionally, we need to test a bit more than usual as well as we need to add an additional fix on top of what Mozilla ships as the solution interferes with one of our patches.
We have a candidate build for testing if you want: https://people.torproject.org/~boklm/builds/8.0.9-build1/ and so far everything looks good. We plan to push the update live in a couple of hours.
Anonymous (not verified) said:
It’s a crappy band-aid! Don…
It’s a crappy band-aid! Don’t put it on us!
Anonymous (not verified) said:
The web site: https://people…
The web site: https://people.torproject.org/~boklm/builds/8.0.9-build1/ blocks connections from Tor exit relays. The web site displays the following message: «Not Found The requested URL /~boklm/builds/8.0.9-build1/ was not found on this server. Apache Server at people.torproject.org Port 443.»
In reply to The web site: https://people… by Anonymous (not verified)
It is not blocking…
It is not blocking connections from Tor: -build1 has been removed as we needed to do a new build. https://people.torproject.org/~boklm/builds/8.0.9-build2/ is the new URL, and soon on https://dist.torproject.org/torbrowser/.
SlimYokozunaFromWWF (not verified) said:
Hey hi Tor team, I just L O…
Hey hi Tor team, I just L O V E your team and work, I appreciate your work a lot. Tor messenger should have been active as well, at least a software which makes any messenger software a Tor messenger, by making changing changes in network setting of a PC. I never used Tor messenger I just think it should have been there.
I always want to donate, I want to donate every now and then. but I think the amount under ‘donate once’ should be lesser than 10$, hmmmm something around 3$ or at the most 5$. for us, we are boomed and banged Chindians. 🙂
Lots of love and respect to you guys!
Jack (not verified) said:
For normal Firefox Users …
For normal Firefox Users (not Tor!) Mozilla released a fixed version: Firefox 66.0.4.
Click help in Firefox, then About and it will update to 66.0.4.
Anonymous (not verified) said:
I’d like the next blog post…
I’d like the next blog post for Tor Browser releases to walk through how to backup and install cleanly. All of these different suggestions to change assorted settings can’t be hygienic for the user base. It’s probably best to serve a guide about it somewhere on the main website or wiki permanently anyway.
Once the bug patch is released, your team deserves a couple full days off. Your weekend was ruined. But thank you all.
Anonymous (not verified) said:
History doesn’t show ip and…
History doesn’t show ip and date of Firefox and the browser communicating over certificates to disable the security feature. Is it in a log somewhere?
I vote for VIV… (not verified) said:
It has mouse gestures,…
It has mouse gestures, keyboard shortcuts built in (both of which makes it a breeze to move between tabs/windows when you have multiple windows with many tabs open; needed, when doing research).
Also has screen shot/page capture, color invert (DARK mode) and many other functionality that are built into the browser, completely eliminating the need to install additional extensions/add-ons.
Anonymous (not verified) said:
In reply to It has mouse gestures,… by I vote for VIV… (not verified)
That’s VIVALDI browser!
That’s VIVALDI browser!
Anonymous (not verified) said:
In reply to It has mouse gestures,… by I vote for VIV… (not verified)
> It has mouse gestures,…
> It has mouse gestures, keyboard shortcuts built in (both of which makes it a breeze to move between tabs/windows when you have multiple windows with many tabs open; needed, when doing research).
Convenience is the enemy of security. I actually hate gestures. I often have the problem that an unintentional gesture maximizes TB, a real no-no. And I have no idea what motions the FF developers intend to be gestures.
Anonymous (not verified) said:
Is it wrong to ask friendly,…
Is it wrong to ask friendly, this error(armagadd-on-2.0) is incredible . braindead only?
Anonymous (not verified) said:
Is this Mozilla certificate…
Is this Mozilla certificate expiration and NoScript disablement a very tasty vulnerability for adversaries to exploit and deanonymize Tor Browser users by creating one or more fake Mozilla add-on certificates now or at some other times in the near or more distant futures? Can a powerful adversary exploit this vulnerability in Tor Browser thanks to the vulnerability caused by the mismanagement of Mozilla certificates for add-ons in Tor Browser? Hasn’t Mozilla already demonstrated a past history on at least one occasion of serious problems in the management of Mozilla certificates for add-ons? Does this indicate Mozilla is wittingly or unwittingly caving on the user security front? Does this mean Tor Browser will be operating with lowered thresholds of user security going into the future? What is the best recourse for worried Tor Browser users operating in countries with dangerous authoritarian governments where communications with the outside world via Tor can bring arrest, torture, imprisonment, or execution at the hands of the state? In light of this exposed compound weakness in Mozilla, NoScript, and Tor Browser, is it risky or dangerous to continue to use Tor Browser if a user faces a powerful and dangerous adversary?
Anonymous (not verified) said:
In reply to Is this Mozilla certificate… by Anonymous (not verified)
> Does this indicate Mozilla…
> Does this indicate Mozilla is wittingly or unwittingly caving on the user security front? Does this mean Tor Browser will be operating with lowered thresholds of user security going into the future?
I am not a coder but I think the answer to those two is «no». But we users are not wrong to be horrified. Seems it could have been much worse, but this should be a wake-up call.
Anonymous (not verified) said:
In reply to Is this Mozilla certificate… by Anonymous (not verified)
This vulnerability was not…
This vulnerability was not triggered by the name on the certificate; it was triggered by the time at which the cert was set to expire.
> by creating one or more fake Mozilla add-on certificates [in the future]?
It would be extremely difficult to deliberately insert a fake Mozilla certificate without anyone noticing; much harder than the cause of this bug. Every certificate in the chain from the top root — ca — production — amo is labeled as being issued by Mozilla Corporation. If you trust what the certificates say, then only Mozilla and the add-on submitter are in the chain. The inclusion of the cert to the Mozilla software repositories is reviewed and then cryptographically signed by Mozilla developers. Tor Project later releases reproducible builds of Tor Browser. If any cert for add-ons is faulty, the browser displays a yellow warning bar.
Hypothetically, it may be simpler to coerce or spearphish a Mozilla developer to compromise the private key. I don’t know if a council of developers observes how their organizational keys are created. I don’t know their methods of holding their organization’s private keys. Mozilla could make a new key to replace a faulty key anyway as quickly as they made the one in the fix.
> Can a powerful adversary exploit this vulnerability in Tor Browser. ?
Which vulnerability? The absence of NoScript can be exploited because individual browser fingerprints became more identifiable on Safer and Safest. The cert chain, however, appears to be totally controlled by Mozilla, no third parties.
> Hasn’t Mozilla demonstrated a past history of serious problems in the management of Mozilla certificates for add-ons?
The recent event was dubbed «armagadd-on 2.0». It was reported about 39 minutes after it expired. The original «armagadd-on» in 2016 was reported about 7 days before it expired.
> Does this indicate Mozilla is wittingly or unwittingly caving on the user security front?
Yes? Unwitting is more likely. People forget expiration dates for all sorts of things. In the world of computing, another example seen very often is when a website domain name is not renewed.
> Does this mean Tor Browser will be operating with lowered thresholds of user security going into the future?
No, definitely higher. 8.0.9 repaired it and is the first step of many toward preventing the problems from happening again.
> What is the best recourse for worried Tor Browser users
Hopefully, when they saw the yellow warning bar, they stopped browsing to new pages and closed Tor Browser or started a New Identity to close all their tabs. Then, hopefully, in the new session, they came straight to this blog to look for updates and help. The basic difference was that their traffic became similar to browsing on Standard. Not exactly, but similar. The good news for at-risk users is that 1) Tor Browser continued using relays as normal, 2) the user’s IP was hidden as normal, 3) the sites they were visiting could only be observed between their exit nodes and destinations as normal. The bad news, mainly, is that those sites and third-parties observing traffic from the exit node could have recorded a browser fingerprint that was more able to relate their traffic to their other traffic despite being from a crowded exit node or a New Identity. If they closed their tabs, their best recourse is to do what they would do similar in manner as if they had been browsing on Standard in that session and until they installed the fix.
> is it risky or dangerous to continue to use Tor Browser
On 8.0.9, it’s as risky as if this bug was never there. As if this bug was recognized and fixed before the cert expired. Just remember to roll back any workarounds you did.
— (not verified) said: