Hardware Root of Trust: Everything you need to know
Last updated on: July 13, 2023 A root of trust is the security foundation for an SoC, other semiconductor device or electronic system. However, its meaning differs depending on who you ask. For example, the hardware root of trust contains the keys for cryptographic functions and is usually a part of the secure boot process providing the foundation for the software chain of trust.
In this article:
-
- What is hardware root of trust?
- What are the types of a silicon-based hardware root of trust?
- What are the benefits of a programmable hardware root of trust?
- What features should a programmable hardware root of trust offer?
- What is the Rambus Root of Trust?
- How is the Rambus Root of Trust architected for security?
- What’s new in the latest generation of Rambus Root of Trust IP?
- What is Quantum Safe Cryptography?
- Is there a Root of Trust configured for my application?
- What should I keep in mind when selecting a Root of Trust IP?
What is hardware root of trust?
A hardware root of trust is the foundation on which all secure operations of a computing system depend. It contains the keys used for cryptographic functions and enables a secure boot process. It is inherently trusted, and therefore must be secure by design. The most secure implementation of a root of trust is in hardware making it immune from malware attacks. As such, it can be a stand-alone security module or implemented as security module within a processor or system on chip (SoC).
What are the types of a silicon-based hardware root of trust?
A silicon-based hardware root of trust falls into two categories: fixed function and programmable. Essentially, a fixed-function root of trust is firmware controlled. These are typically compact and designed to perform a specific set of functions like data encryption, certificate validation and key management. These compact, firmware-controlled root of trust solutions are particularly well suited for Internet of Things (IoT) devices.
In contrast, a hardware-based programmable root of trust is built around a CPU. Performing all the functions of a firmware-controlled solution, a programmable root of trust can also execute a more complex set of security functions. A programmable root of trust is versatile and upgradable, enabling it to run entirely new cryptographic algorithms and secure applications to meet evolving attack vectors.
What are the benefits of a programmable hardware root of trust?
The cybersecurity threat landscape is dynamic and rapidly evolving. Indeed, attackers are constantly finding new ways to exploit critical vulnerabilities across a wide range of applications and devices. Fortunately, a programmable hardware-based root of trust can be continuously updated to contend with an ever-increasing range of threats.
A programmable hardware-based root of trust is a key component to protect against a number of security threats, including:
- Host processor compromise
- Non-volatile memory (NVM) key extraction
- Tearing and other attacks against NVM writes
- Corruption of non-volatile memory or fuses
- Test and debug interface attacks
- Side-channel and perturbation attacks including Simple Power Analysis (SPA), Differential Power Analysis (DPA) and Fault Injection Attacks (FIA)
- Manufacturing/personalization facility compromise (insider attack)
- Man-in-the-middle and replay attacks
- Probing of external buses
What features should a programmable hardware root of trust offer?
A programmable hardware root of trust should be purpose-built; specifically designed from the ground up to provide a robust level of security. Since the root of trust is a logical target for an attacker, it should be made as secure as possible to safeguard it from compromise. Capabilities should include:
Siloed Execution:
Comprehensive Anti-Tamper and Side-Channel Resistance:
Layered Security:
Multiple Root of Trust Instances:
What is the Rambus Root of Trust?
Rambus offers a catalog of robust Root of Trust solutions, ranging from richly featured military-grade co-processors to highly compact firmware-controlled. With a breadth of solutions applicable from the data center to IoT devices, Rambus has a Root of Trust solution for almost every application.
How is the Rambus Root of Trust architected for security?
The Rambus RT-600 series of Root of Trust hardware IP cores is built around Verilog RTL, which enables the customizable and modular root of trust to be easily integrated in any chip or FPGA design. Perhaps most importantly, the Rambus RT-600’s layered architecture provides the security of a hardware design with the flexibility of software.
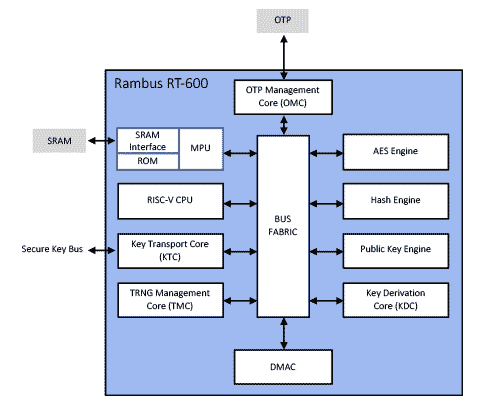
Simplified Rambus RT-600 Series Root of Trust Block Diagram
The diagram above illustrates the basic architecture of the Rambus RT-600 series Root of Trust, including:
Purpose-built 32-bit CPU:
Multiple Bus Fabrics:
Private SRAM:
Key Transport Core:
True Random Number Generator:
DMA Controller:
Key Derivation Core:
Cryptographic Engines:
OTP Management Core:
As noted above, the versatile Rambus RT-600 series Root of Trust can be easily integrated into a wide range of silicon. Its standard interfaces include AMBA interface buses for communicating with registers (the control plane interface into the core), as well as an AHB bus that interfaces with system memory (data plane access). The Rambus RT-600 series Root of Trust also offers easy-to-use test interfaces of key buses for supplying keys to external logic, as well as I/O pins for managing various functions like chip features and alerts (controlling and monitoring external logic).
Additional key Rambus Root of Trust security features and capabilities include:
Self-Contained Secure Boot Mechanism:
Side-Channel Resistance:
Glitch and Fault Injection Attack Protection:
Memory Protection Unit:
Private SRAM and Isolated CPU Bus:
The Rambus RT-600 series Root of Trust – which includes a complete firmware stack – also employs a layered security model for software utilizing privilege levels that are part of the RISC-V ISA. Put simply, these privilege levels are enforced on a hardware level, thereby effectively separating data between their respective layers. More specifically, the least privileged (least secure) layer is the user level, which is where user-written secure applications run. These applications can also be referred to as containers.
The next level is the supervisor level, where a Zephyr-based microkernel customized for security resides and runs. As expected, the highest privilege level is where the most secure code runs, with a security monitor overseeing the microkernel and containers, as well as their interaction with hardware. Although lower levels are more flexible, they are considered less secure. As such, the security monitor is specifically designed to provide a robust level of security protection for the software stack.
What’s new in the latest generation of Rambus Root of Trust IP?
This latest generation of the RT-600 Root of Trust series offers many new features designed to support the security needs of customers today and into the future.
Amongst the new architectural and security features are:
- A AXI4 master interface with 64-bit address
- Caliptra Root of Trust for Measurement (RoTM) with DICE and X.509 support
- A new secure data store mechanism
- A Quantum Safe Engine (QSE) with CRYSTALS-Kyber and CRYSTALS-Dilithium
- Extended Physical Unclonable Function (PUF) support via an internal PUF, as well as an optional external PUF
What is Quantum Safe Cryptography?
The RT-600 Root of Trust series is at the forefront of a new category of programmable hardware-based security cores with its new Quantum Safe Cryptography features.
Once sufficiently powerful quantum computers exist, traditional asymmetric cryptographic methods for key exchange and digital signatures will be easily broken. New cryptographic algorithms known as quantum safe cryptography (QSC) or post-quantum cryptography (PQC) are needed to protect against quantum computer attacks.
The latest generation of Rambus Root of Trust IP offers a state-of-the-art programmable security solution to protect hardware and data with NIST and CNSA quantum-resistant algorithms. The Quantum Safe Engine operates with the CRYSTALS-Kyber and CRYSTALS-Dilithium algorithms, as well as the stateful hash-based signature schemes XMSS (eXtended Merkle Signature Scheme) or LMS (Leighton-Micali Signatures).
Is there a Rambus Root of Trust configured for my application?
There are Rambus Root of Trust solutions tailored to address the specific security requirements and certification standards of nearly every application:
- The RT-100 series of Root of Trust solutions are designed for use in power and space-constrained applications as in IoT devices. Featuring a firmware-controlled architecture with dedicated secure memories, the RT-100 hardware Root of Trust cores provides a variety of cryptographic accelerators including AES, SHA-2, RSA and ECC. There are versions which include SM2, SM3 and SM4 accelerators for the China market.
- The RT-630 is a fully programmable, FIPS 140-3 compliant, hardware security core offering security-by-design for data center cloud, AI/ML, as well as general purpose semiconductor applications. It protects against a wide range of hardware and software attacks through state-of-the-art anti-tamper and security techniques. There are versions of the RT-630 tailored to the China (RT-631) and IoT (RT-632) markets, and the RT-634 includes a Quantum Safe Engine.
- The RT-640 and RT-645 are tailored for the automotive market offering ISO-26262 ASIL-B and ASIL-D implementations respectively. These support vehicle-to-vehicle and vehicle-to-infrastructure (V2X), advanced driver-assistance systems (ADAS) and infotainment uses. The RT-641 is ASIL-B compliant and includes the SM2, SM3 and SM4 accelerators for the China market.
- For highly-secure data center and government-focused chip designs, the RT-650 and RT-660 are FIPS 140-3 compliant and offer DPA and FIA protection respectively. There are versions of the RT-650 and RT-660 that include a Quantum Safe Engine.
- CryptoCell and CryptoIsland Root of Trust solutions are programmable, FIPS 140-3 certifiable hardware security modules. They are designed to be integrated into Arm TrustZone-based SoCs or FPGAs where power and space are a consideration.
What should I keep in mind when selecting a Root of Trust IP?
- What is the end use of the chip?
- Who and what are you protecting against?
- What is the risk of a compromised device?
- What certifications are required?
It’s also worth noting that Root of Trust products can be tailored to match an applications security threat model, use case, industry segment, lifetime, cost, and geography. Some examples of the different criteria that can be selected include the crypto algorithms, security/anti-tamper mechanisms, and provisioning methods used.
Oracle Cloud Infrastructure Hardware Root of Trust
Reduce the risk of firmware-based attacks against Oracle Cloud Infrastructure customer tenants with custom-built, hardware-based root of trust technology.
Learn about security-first design principles
See how security is fundamental to the architecture of Oracle Cloud Infrastructure with tiered defenses and highly secure operations.
Oracle Cloud Infrastructure Hardware Root of Trust
Hardware technology customized to deploy clean firmware for every new tenancy
Reduce the risk of firmware-level attacks against cloud tenants with root of trust technology designed to wipe and reinstall the firmware every time a new server is provisioned or a new customer tenancy is established.
Cleans and power cycles each new server
Reduces the risk from a permanent denial of service (PDoS) attack or attempts to embed backdoors in the firmware by power cycling the hardware host, installing the firmware, and confirming the process has been performed as expected for every new server.
January 6, 2020
Security Must Be Easier and Not Just for the Experts
Paul Toal, Distinguished Solution Engineer, Cybersecurity, Oracle
Security is hard. If you look at Oracle’s security portfolio, we have a fantastic set of mature capabilities, providing defense-in-depth through layered security, from securing the data through to the users, platforms, and applications. We have worked hard to provide market-leading products and tools in all of the areas that we operate, and continue to do so.
Featured blogs
Resources

Oracle Cloud Free Tier
Build, test, and deploy applications on Oracle Cloud for free. Sign up once, get access to two free offers.
Вы отправили слишком много запросов, поэтому ваш компьютер был заблокирован.
Для того, чтобы предотвратить автоматическое считывание информации с нашего сервиса, на Linguee допустимо лишь ограниченное количество запросов на каждого пользователя.
Пользователям, браузер которых поддерживает Javascript, доступно большее количество запросов, в отличие от пользователей, чей браузер не поддерживает Javascript. Попробуйте активировать Javascript в настройках вашего браузера, подождать несколько часов и снова воспользоваться нашим сервером.
Если же ваш компьютер является частью сети компьютеров, в которой большое количество пользователей одновременно пользуется Linguee,сообщитеоб этом нам.What is a root of trust?
When a user registers on a website the device platform offers the user several options to start their journey. The user may be offered to use either an external authenticator, such as a hardware security key, or an internal authenticator built into the OS platform itself, such as a fingerprint touchpad on the user’s laptop, to secure their new account. The best practice is first use the external authenticator before enabling the internal authenticator.
Greater user choice and control
During the registration process, a credential is created which is stored on the authenticator of choice. For fast recovery and bootstrapping of a new device it is recommended that the user always first register using the external authenticator, such as a hardware security key, and then bootstrap the internal authenticator using the external key. If a device is lost the security key credential is still usable on a replacement device, unlike the built-in authenticator which is no longer accessible if the device is lost. Once this has been completed, the user can authenticate to the web service or other resources using whichever authenticator they prefer on a day-to-day basis.
Fast-track onboarding a new device or account recovery
If the user wants to add a new device to authenticate to the web service, or in the event of a lost or stolen device, having a portable root of trust, such as a security key, greatly accelerates the onboarding and account recovery process. The user no longer needs cellular connectivity, or to wait for SMS codes to be sent from each web service, or to enter multi-digit codes one by one for each web service. With a security key a user can quickly insert the key into the USB port of a laptop or desktop, simply tap a mobile device and instantly be re-authenticated to a variety of web services quickly and efficiently, without any need for cellular connectivity or calls to the helpdesk.