Cisco IOS Internal VLANs
Небольшая заметка о том, что происходит «под капотом» MLS (Multi Layer Switch) Cisco при создании routed интерфейсов.
В MLS интерфейс может находиться в одном из двух режимов:
- «switchport»
- «routed interface» или «no switchport»
При переводе интерфейса в последний, коммутатор позволяет присвоить ip address непосредственно порту и использовать его как интерфейс маршрутизатора.
Однако это всего лишь абстракция. Вот что происходит «под капотом» MLS при переводе интерфейса в режим «no switchport»:
- коммутатор создает VLAN
- коммутатор добавляет интерфейс в этот VLAN в режиме access. Это будет единственный интерфейс, принадлежащий данному VLAN
- коммутатор создает SVI (Switch Virtual Interface) для выбранного VLAN и присваивает указанный ip address данному SVI
Фактически следующие две конфигурации почти идентичны*:
interface Ethernet0/0 no switchport ip address 10.0.0.1 255.255.255.0interface Ethernet0/0 switchport mode access switchport access vlan 100 interface Vlan 100 ip address 10.0.0.1 255.255.255.0*если у коммутатора больше нет ни одного access интерфейса, принадлежащего VLAN 100, и VLAN 100 не разрешен ни на одном из trunk интерфейсов.
Возьмем в качестве примера коммутатор с минимальной стартовой конфигурацией. Все интерфейсы находятся в режиме switchport и принадлежат VLAN 1:
SW1#sh interfaces status Port Name Status Vlan Duplex Speed Type Et0/0 connected 1 auto auto unknown Et0/1 connected 1 auto auto unknown Et0/2 connected 1 auto auto unknown Et0/3 connected 1 auto auto unknown SW1#sho vlan brief VLAN Name Status Ports ---- -------------------------------- --------- ------------------------------- 1 default active Et0/0, Et0/1, Et0/2, Et0/3 1002 fddi-default act/unsup 1003 token-ring-default act/unsup 1004 fddinet-default act/unsup 1005 trnet-default act/unsupПереведем интерфейс Ethernet 0/0 в routed режим:
SW1#conf t Enter configuration commands, one per line. End with CNTL/Z. SW1(config)#interface ethernet 0/0 SW1(config-if)#no switchport SW1(config-if)#end SW1#show running-config interface ethernet 0/0 Building configuration. Current configuration : 59 bytes ! interface Ethernet0/0 no switchport no ip address endVLAN, который создается при переводе интерфейса в routed режим не виден в обычной БД VLAN:
SW1#sho vlan brief VLAN Name Status Ports ---- -------------------------------- --------- ------------------------------- 1 default active Et0/0, Et0/1, Et0/2, Et0/3 1002 fddi-default act/unsup 1003 token-ring-default act/unsup 1004 fddinet-default act/unsup 1005 trnet-default act/unsupНо его можно увидеть среди «Internal VLANs»:
SW1#show vlan internal usage VLAN Usage ---- -------------------- 1006 Ethernet0/0Потенциальная проблема такого поведения коммутатора
Поскольку теперь VLAN ID 1006 занят под Internal VLAN для интерфейса Ethernet0/0, не получится создать VLAN с таким же ID, а значит SW1 не сможет коммутировать трафик в этом VLAN:
SW1#conf t Enter configuration commands, one per line. End with CNTL/Z. SW1(config)#vlan 1006 SW1(config-vlan)# SW1(config-vlan)#exit % Failed to create VLANs 1006 VLAN(s) not available in Port Manager. %Failed to commit extended VLAN(s) changes. *Jan 5 17:34:31.407: %PM-4-EXT_VLAN_INUSE: VLAN 1006 currently in use by Ethernet0/0 *Jan 5 17:34:31.407: %SW_VLAN-4-VLAN_CREATE_FAIL: Failed to create VLANs 1006: VLAN(s) not available in Port ManagerОднако у этой проблемы есть довольно простое решение:
- нужно выключить L3-интерфейс (shutdown), при этом Internal VLAN ID освободится
- далее создаем VLAN с нужным ID
- включаем L3-интерфейс ( no shutdown), коммутатор займет следующий свободный VLAN ID из Extended диапазона
SW1#conf t Enter configuration commands, one per line. End with CNTL/Z. SW1(config)#inter ethernet 0/0 SW1(config-if)#shutdown Как выбирается VLAN ID для L3 интерфейса
В стартовой конфигурации любого коммутатора есть следующая строка:
! vlan internal allocation policy ascending !Это означает, что коммутатор использует первый свободный VLAN ID из Extended диапазона: 1006 — 4094.
Поскольку в нашем примере VLAN ID 1006 занят, а VLAN 1007 используется для L3 интерфейса Ethernet0/0, то если перевести еще один интерфейс в режим routed, коммутатор выделит для него VLAN ID 1008:
SW1#conf t Enter configuration commands, one per line. End with CNTL/Z. SW1(config)#inter ethernet 0/3 SW1(config-if)#no switchport SW1(config-if)#end SW1#show vlan internal usage VLAN Usage ---- -------------------- 1007 Ethernet0/0 1008 Ethernet0/3Теперь создадим VLAN 1009, и после этого переведем еще один интерфейс в routed режим, поскольку VLAN 1009 занят, коммутатор использует следующий свободный VLAN для L3 интерфейса — 1010:
SW1#conf t Enter configuration commands, one per line. End with CNTL/Z. SW1(config)#vlan 1009 SW1(config-vlan)#end W1#sho vlan brief VLAN Name Status Ports ---- -------------------------------- --------- ------------------------------- 1 default active Et0/2 1002 fddi-default act/unsup 1003 token-ring-default act/unsup 1004 fddinet-default act/unsup 1005 trnet-default act/unsup 1006 VLAN1006 active 1009 VLAN1009 active SW1#conf t Enter configuration commands, one per line. End with CNTL/Z. SW1(config)#inter ethernet 0/2 SW1(config-if)#no sw SW1(config-if)#no switchport SW1(config-if)#end SW1#sho vlan internal usage VLAN Usage ---- -------------------- 1007 Ethernet0/0 1008 Ethernet0/3 1010 Ethernet0/2Некоторые платформы позволяют изменить политику выбора номеров для Internal VLAN, хотя большинство устройств поддерживают только один вариант — ascending:
SW1(config)#vlan internal allocation policy ? ascending Allocate internal VLAN in ascending order Что происходит при создании L3 Port-channel
Для каждого member интерфейса выделяется свой Internal VLAN ID, для самого Port-channel интерфейса выделяется еще один Internal VLAN ID:
Вернем коммутатор в стартовую конфигурацию: SW1#sho inter status Port Name Status Vlan Duplex Speed Type Et0/0 connected 1 auto auto unknown Et0/1 connected 1 auto auto unknown Et0/2 connected 1 auto auto unknown Et0/3 connected 1 auto auto unknown SW1#sho vlan inter SW1#sho vlan internal usa SW1#sho vlan internal usage VLAN Usage ---- -------------------- SW1# SW1(config)#inter range ethernet 0/0 - 1 SW1(config-if-range)#no switchport SW1(config-if-range)#do show vlan internal usage VLAN Usage ---- -------------------- 1006 Ethernet0/0 1007 Ethernet0/1 SW1(config-if-range)#channel-group 1 mode active Creating a port-channel interface Port-channel 1 SW1(config-if-range)#do show vlan internal usage VLAN Usage ---- -------------------- 1006 Ethernet0/0 1007 Ethernet0/1 1008 Port-channel1Если после этого выключить и заново включить Port-channel интерфейс (при этом то же самое происходит и со всеми member интерфейсами), то соответствие интерфейсов и Internal VLAN ID может измениться:
SW1(config-if-range)#inter po1 SW1(config-if)#shutdown SW1(config-if)#do show vlan internal usage VLAN Usage ---- -------------------- SW1(config-if)#no shutdown SW1(config-if)#do show vlan internal usage VLAN Usage ---- -------------------- 1006 Port-channel1 1007 Ethernet0/0 1008 Ethernet0/1P.S.
При создании Loopback интерфейсов Internal VLAN не создается.
Vlan internal allocation policy ascending cisco что это
Итак приведем схему используемого оборудования.
Как видно из рисунка ниже, в основе сети удаленного офиса находится маршрутизатор Cisco Catalyst 3750G-12S.
В качесте уровня доступа используем коммутаторы Cisco Catalyst 2960.
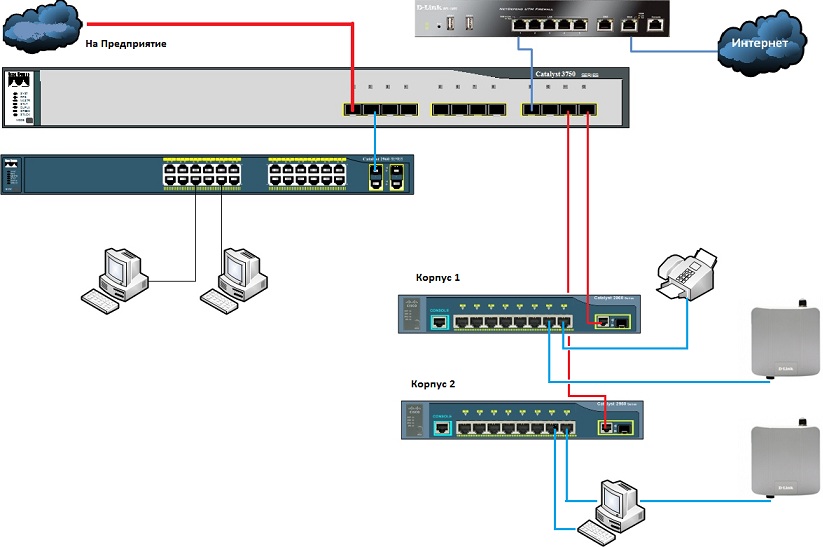
Настройки маршрутизатора - следующие:
!
hostname ROfice_Core
!
switch 1 provision ws-c3750g-12s
vtp mode transparent
ip subnet-zero
ip routing
no ip dhcp conflict logging
ip dhcp excluded-address 192.168.11.200 192.168.11.254
ip dhcp excluded-address 192.168.33.200 192.168.33.254
!
ip dhcp pool Internet
network 192.168.11.0 255.255.255.0
dns-server 83.149.22.14 83.149.22.15
default-router 192.168.11.1
!
ip dhcp pool Campus
network 192.168.33.0 255.255.255.0
dns-server 10.4.5.99 10.4.5.81
default-router 192.168.33.1
netbios-name-server 10.4.5.218
lease 30
!
На маршрутизаторе настроили сервис DHCP для двух зон:
192.168.11.0 255.255.255.0
192.168.33.0 255.255.255.0
Заводим Vlan - используемые на сетях WI-FI.
!
no file verify auto
spanning-tree mode pvst
spanning-tree extend system-id
!
vlan internal allocation policy ascending
!
vlan 11
name ROfice_Only_Internet_User
!
vlan 33
name ROfice_Campus_User
!
Заводим Vlan - Управления и для пользователей.
!
vlan 232
name ROfice_Mgmt
!
vlan 233
name ROfice_User
!
Все интерфейсы кроме 9 настраиваем на транк:
!
interface GigabitEthernet1/0/1
switchport trunk encapsulation dot1q
switchport mode trunk
!
interface GigabitEthernet1/0/2
switchport trunk encapsulation dot1q
switchport mode trunk
!
. . .
!
interface GigabitEthernet1/0/9
no switchport
ip address 192.168.12.1 255.255.255.0
!
interface GigabitEthernet1/0/10
switchport trunk encapsulation dot1q
switchport mode trunk
!
interface GigabitEthernet1/0/11
switchport trunk encapsulation dot1q
switchport mode trunk
!
interface GigabitEthernet1/0/12
switchport trunk encapsulation dot1q
switchport mode trunk
!
interface Vlan1
no ip address
!
interface Vlan11
ip address 192.168.11.1 255.255.255.0
ip helper-address 192.168.33.200
!
interface Vlan33
ip address 192.168.33.1 255.255.255.0
ip helper-address 192.168.33.200
!
interface Vlan232
ip address 172.16.232.3 255.255.255.0
no ip mroute-cache
!
!
ip default-gateway 172.16.232.254
ip classless
ip route 0.0.0.0 0.0.0.0 192.168.12.2
ip route 10.0.0.0 255.0.0.0 172.16.232.254
ip route 172.16.0.0 255.255.0.0 172.16.232.254
ip http server
Настройка коммутатора следующая:
!
hostname ROfice_Cross
!
!
spanning-tree mode pvst
spanning-tree extend system-id
!
vlan internal allocation policy ascending
!
vlan 11,33
!
vlan 232
name ROfice_Mgmt
!
vlan 233
name R)fice_User
!
!
interface FastEthernet0/1
switchport access vlan 233
spanning-tree portfast
!
. . .
!
interface FastEthernet0/24
switchport access vlan 233
spanning-tree portfast
!
interface Vlan1
no ip address
no ip route-cache
!
interface Vlan232
ip address 172.16.232.10 255.255.255.0
no ip route-cache
!
ip default-gateway 172.16.232.254
ip http server
ip http secure-server
!
Настройка корпусных коммутаторов следующая:
!
hostname ROfice_Korpus_1
!
!
spanning-tree mode pvst
spanning-tree extend system-id
!
vlan internal allocation policy ascending
!
vlan 11,33
!
vlan 232
name ROfice_Mgmt
!
vlan 233
name ROfice_User
!
!
interface FastEthernet0/1
switchport trunk native vlan 33
switchport mode trunk
spanning-tree portfast
!
. . .
!
interface FastEthernet0/7
switchport access vlan 33
spanning-tree portfast
!
interface FastEthernet0/8
switchport access vlan 33
spanning-tree portfast
!
interface GigabitEthernet0/1
switchport mode trunk
!
interface Vlan1
no ip address
no ip route-cache
!
interface Vlan232
ip address 172.16.232.11 255.255.255.0
no ip route-cache
!
ip default-gateway 172.16.232.254
ip http server
ip http secure-server
!
The fairy tale of the VLAN internal allocation policy

This conf command! You can find him in CatOS and on more recent IOS Cisco firmware.
When we configure a routed-port on a Cisco switch:
CatLab01(config)#int gi0/3 CatLab01(config-if)#no switchport CatLab01(config-if)#ip address 172.29.29.1 255.255.255.0We tell our L2 device to act as a router on that port. But the Switch is not a Router so it may have a dedicated L2 VLAN to segregate the broadcast domain.
We can decide only ascending (from 1006 to 4094) or descending (from 4094 to 1006) VLAN id of the policy but we will never see them in our vlan -database. If we accidentally overlap these reserved VLANs we receive this message:
%Failed to create VLANs 1006
VLAN(s) not available in Port Manager.
%Failed to commit extended VLAN(s) changes.
The only way to verify the use of internal vlan is the following command:
CatLab01#sh vlan internal usage VLAN Usage ---- -------------------- 1006 GigabitEthernet0/3REMEMBER when you do vlan planning!
In the datacenter and backhaul networks where many vlans are needed, it would be better to avoid using this feature. It is preferable to have a dedicated router to manage L3 links and let the switches do their L2 job.
more information con Cisco Community
device involved: Cisco 3800, Cisco 3700, Cisco 2400
… this were the VLAN tale.
IP Routing and Switching
If you have worked with Cisco switches for some time you may have noticed this command when viewing the configuration. Ever wonder what it actually means?
Well, I have and today I just so happened to satisfy my own curiosity by looking it up.
In short, it means that the switch will allocate VLANS for internal use starting from VLAN 1006 (because VLAN 1002-1005 are reserved for some legacy stuff that nobody dares remove even though the calendar says 2014).
This may make you go "Oh. Well, of course, that's what it means. " and think no more of it. But, if you are anything like me, you probably went "Ok. What does that mean?". What are VLANS used for "internally" on a Cisco switch?
One example that is easy to setup in the lab is this:
SW01(config)#int gi0/33
SW01(config-if)#no switchport
SW01(config-if)#ip address 192.168.1.1 255.255.255.0
We just changed a switchport on a Catalyst switch into a routed port. Another way of accomplishing this goal would be to do this:
SW01(config)#int gi0/33
SW01(config-if)#switchport access vlan 10
% Access VLAN does not exist. Creating vlan 10
SW01(config-if)#int vlan 10
SW01(config-if)#ip address 192.168.1.1 255.255.255.0
Assuming that interface gi0/33 is the only interface in VLAN 10 - this would pretty much accomplish what the no switchport command does. In fact, it is exactly what the no switchport command does and the vlan internal is the key to show it.
Let us look at the no switchport scenario and see if we can't peek a little behind the curtains.
SW01#show ip interface brief | include GigabitEthernet0/33
GigabitEthernet0/33 192.168.1.1 YES manual down down
So, the interface has an IP address assigned manually and it is currently in the down-down state (no cable is attached). Let us try to see some of the internal vlan usage.
SW01#sh vlan internal usage
VLAN Usage
---- --------------------
1006 GigabitEthernet0/33
This shows us that VLAN 1006 has been assigned to GigabitEthernet0/33 (per the allocation policy).
So, what this means is, that when you issue the no switchport command, the switch creates VLAN 1006 and assigns it the IP address and chains it to the physical interface.
A thing to keep in mind is that internally assigned VLANs and user created VLANs share the same database so an error message like the one below is shown if I try to manually create a VLAN that is already assigned internally.
SW01(config)#vlan 1006
SW01(config-vlan)#exit
% Failed to create VLANs 1006
VLAN(s) not available in Port Manager.
%Failed to commit extended VLAN(s) changes.
*Jun 10 08:20:11.932: %PM-4-EXT_VLAN_INUSE: VLAN 1006 currently in use by GigabitEthernet0/33
*Jun 10 08:20:11.932: %SW_VLAN-4-VLAN_CREATE_FAIL: Failed to create VLANs 1006: VLAN(s) not available in Port Manager
You can probably imagine some of the scenarios that might arise if you don't know that this is the way Catalyst switches accomplishes this - maybe you have your own tale to tell on the subject.
Here is a link to an article about one of the more likely situation you might learn of this "feature" in the IOS: http://packetpushers.net/cisco-internal-vlan-usage/
Edit (27-10-2014):
There are a few more things that the no switchport command disables.
You can mimic the no switchport a little better if you issued the following commands:
SW01(config)#no spanning-tree vlan 10
SW01(config)#no mac address-table learning vlan 10
SW01(config)#interface gi0/33
SW01(config-if)#switchport mode access
SW01(config-if)#switchport access vlan 10
SW01(config-if)#switchport nonegotiate
SW01(config-if)#no vtp
SW01(config-if)#exit
SW01(config)#interface vlan 10
SW01(config-if)#ip address 192.168.1.1 255.255.255.0
This disables spanning-tree and mac learning on the vlan, adds the port to the vlan as an access port, disables DTP negotiation and VTP on the port and finally configures an IP address on the SVI (switched virtual interface).